
 By Basiran
A teenager from Amman, Jordan, suspected of operating as a central figure within the prolific data theft and extortion collective known as ShinyHunters, has been detained by local authorities and is reportedly cooperating with the FBI to identify other members of the hacking syndicate.
According to information obtained by KrebsOnSecurity, the suspect—who operates under the hacker handle "Rey"—was taken into custody just as ShinyHunters was actively engaged in extorting a business unit recently divested by global aerospace giant Boeing. In a striking convergence of cybercrime and personal proximity, the target of this latest extortion plot manufactures the fleet of aircraft utilized by the employer of Rey’s father: Royal Jordanian Airlines.
The Capture of "Rey" and International Arrests
The detention of the suspect, identified by Reuters and security researchers as Saif Al-din Khader, marks a major development in the international crackdown on modern data-extortion gangs. On October 3, Reuters cited three unnamed sources confirming that Khader had been detained by Jordanian authorities and was actively assisting the FBI. KrebsOnSecurity had previously identified Rey as Khader in a November 2025 investigative profile, during which the young man openly admitted to collaborating with multiple ransomware operations.
Rey’s activities were thrust back into the spotlight following a September 28 exclusive detailing the Dutch police’s arrest of 24-year-old convicted cybercriminal Pepijn van der Stap. Authorities suspect Van der Stap of aiding ShinyHunters in their data theft and extortion schemes.
According to security reports, immediately following the Dutchman’s arrest on the evening of September 15, Rey assumed direct control over the ShinyHunters brand. In the wake of this takeover, he publicly boasted about stealing highly sensitive data from the FBI and extorting the notorious ransomware syndicate known as Cl0p.
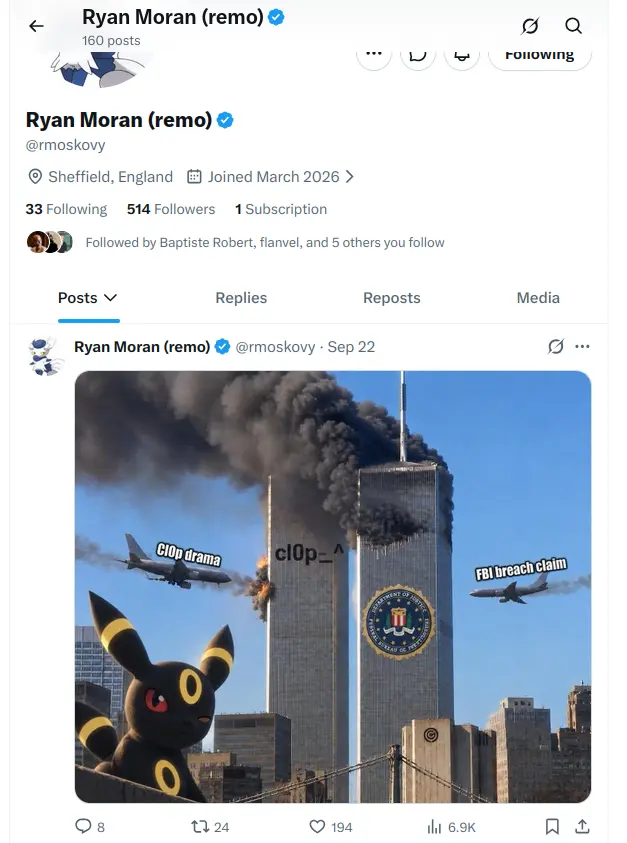
Rather than keeping a low profile, Rey actively taunted both the FBI and Cl0p by publishing memes to his long-standing Twitter/X account. Bizarrely, he embedded images of the avatar used by Van der Stap’s former hacker alias, "Umbreon," in an apparent attempt to frame the imprisoned Dutchman for the newly launched attacks.

Exploiting the Oracle PeopleSoft Vulnerability
The resurgence of the ShinyHunters brand relied heavily on the mass exploitation of enterprise software. As detailed in previous security advisories, the group gained unauthorized access to the FBI recruitment website and numerous other victim networks by exploiting a critical zero-day vulnerability, designated CVE-2026-35273, in Oracle PeopleSoft.
PeopleSoft is a widely utilized software-as-a-service platform that organizations across the globe depend on for human resources management, payroll administration, and hiring processes. Oracle moved quickly to issue a patch after ShinyHunters began weaponizing the flaw in June. Simultaneously, cybersecurity firm Mandiant released web application firewall (WAF) rules designed to protect organizations that could not immediately apply the security update.
While ShinyHunters admitted to BleepingComputer in June that their initial goal was to breach the FBI’s proprietary PeopleSoft database—an attempt they claimed was ultimately unsuccessful—the group later adapted. In subsequent weeks, they deployed a well-known URL-encoding trick to bypass the WAF rules recommended by Mandiant.
A joint threat intelligence report released on September 25 by Mandiant and the Google Threat Intelligence Group (GTIG) confirmed that ShinyHunters had mass-exploited the PeopleSoft vulnerability. The campaign compromised dozens of systems spanning diverse industries, including healthcare, higher education, technology, transportation, agriculture, and government agencies.
The fallout from these intrusions has been severe. Reuters reported that the FBI removed an Accenture contractor over their failure to patch the recruitment portal. The breach exposed sensitive personal data belonging to more than 5,000 FBI personnel, including specialized unit assignments, psychiatric records, and medical histories.
"Rey" Means King, As in Royal
According to two sources familiar with the ongoing international investigation into ShinyHunters, a digital aviation and navigation unit recently divested by Boeing was directly targeted in the extortion campaign underway at the time of Rey’s apprehension. The FBI’s investigation gained renewed urgency due to this specific target, as the stolen data reportedly posed potential operational safety and security risks.

Boeing acknowledged the extortion attempts in a statement, confirming that the incident involved data stolen from Jeppesen ForeFlight. Boeing had previously sold this subsidiary in November 2025 to the private equity firm Thoma Bravo for $10.55 billion.
"We are aware of claims by a threat actor regarding data allegedly associated with Boeing and our former subsidiary Jeppesen ForeFlight," a Boeing spokesperson stated, noting that the company is actively reviewing the situation. Jeppesen ForeFlight added that an internal investigation revealed no operational or product impact.
Rey’s alleged role in targeting the former Boeing unit carries deep ironical weight given his familial ties. Strong evidence indicates his father is employed by Royal Jordanian Airlines, a carrier predominantly controlled by the Jordanian government that relies on Boeing aircraft for its long-haul operations. Although Rey claimed on Telegram in early 2025 that his father was an airline pilot—a claim that could not be independently verified—data recovered from a password-stealing malware infection on the family’s shared computer showed his father using identical credentials across multiple Royal Jordanian Airlines employee portals.
Neither Rey nor his father responded to requests for comment sent by KrebsOnSecurity prior to the publication of these findings. However, within hours of the outreach, Rey systematically deleted his various social media profiles, including the Twitter/X account used to taunt the FBI and Cl0p.
Despite the digital purge, Rey’s GitHub cybersecurity blog remained online, revealing a fixation on the leadership of the Cl0p ransomware operation. A lengthy post published on the blog in March 2026 went so far as to doxe two Russian men alleged to be the core developers and hackers behind Cl0p.
Explosive Allegations in the Netherlands
While the investigation into the teenage administrator unfolds in Jordan, Dutch media has brought to light separate, explosive allegations against Pepijn van der Stap. Despite his public rebranding as a reformed hacker who had put his criminal past behind him, the Dutch daily RTL reported on September 29 that investigators suspect Van der Stap attempted to orchestrate at least two murders abroad.

Van der Stap had recently completed the majority of a four-year prison sentence for data theft and extortion activities that prosecutors estimated netted between 1.5 million and 2.7 million euros. Following his release, he secured a position as an "offensive security lead" at Neo Security, a Dutch cybersecurity firm where he purportedly tested client networks for vulnerabilities.
Benjamin Korper, the owner of Neo Security, told Reuters that he hired an independent firm to investigate whether Van der Stap had compromised his company or its clients, though no evidence of internal malicious activity has surfaced. Korper confirmed that Dutch forensic investigators descended upon his office on September 15 during the dramatic police raid that resulted in Van der Stap’s arrest, an operation that reportedly involved the use of flash-bang grenades.
Before his initial 2023 arrest, Van der Stap worked as a software engineer for Amsterdam-based cybersecurity startup Hadrian and volunteered with the Dutch Institute for Vulnerability Disclosure (DIVD), maintaining a facade of legitimacy while actively extorting major corporations. When previously interviewed about how the public could trust his claims of reform, Van der Stap maintained that his remediation efforts spoke for themselves, noting that critics would believe what they chose to believe regardless of his statements.
Franchising and Burning a Brand
Cybercriminals operating under the ShinyHunters banner have been linked to dozens of major data breaches stretching back to 2019, accounting for billions of stolen records. However, security experts emphasize that the individuals currently wielding the ShinyHunters moniker are distinct from the group’s original core members, most of whom are French citizens who have previously faced arrest and imprisonment.
In practice, ShinyHunters has evolved into a franchise model. Security analysts liken the structure to the fictional character Dread Pirate Roberts from The Princess Bride, where succession occurs via arrest rather than death, and multiple individuals may claim the mantle simultaneously. Investigators note that the FBI’s current focus centers on a network of freelance cybercriminals and affiliates who supply stolen SaaS platform credentials in exchange for a cut of subsequent ransom payments.
Following Van der Stap’s arrest, a Telegram chat server allegedly run by Rey became a hub of criticism. Participants mocked the teenager after he backed down from public threats against the FBI and Cl0p, a retreat that coincided with the sudden offline status of the ShinyHunters darknet website. Commentators accused Rey of co-opting the established brand name following the arrests of its French founders to run extortion schemes and peddle stolen data for personal profit.

Administrators of a rival Telegram channel dedicated to exposing alleged hackers echoed these sentiments, writing that Rey made a critical error by trying to resurrect a dismantled criminal brand. According to community estimates cited on the channel, Rey’s activities generated significant digital disruption while netting him a 25 to 30 percent cut from collaborative extortion negotiations.
The group’s operational motivations were further highlighted in an interview with The Register, where ShinyHunters claimed their decision to target the FBI was a calculated public relations maneuver. The hackers asserted that the hack was designed to counter a May 2026 FBI flash notice that advised victims against paying ransoms and warned of aggressive harassment tactics, including threatening phone calls and swatting.
While the hackers argued that breaching the agency demonstrated their technical proficiency and discredited official warnings, security analysts point out that these high-profile antics ultimately invited intense international scrutiny, culminating in the coordinated arrests and detentions that continue to dismantle the network.
 Nila Kartika Wati
 Sagoh
 Dwi Wanna