
 By Nana Wu
As financial charts across the digital asset landscape flip from red to green, the decentralized finance sector is experiencing a remarkable resurgence. Crypto lending, in particular, has seen a powerful renewed wave of interest and capital influx after navigating a particularly dismal second quarter that shook market confidence.
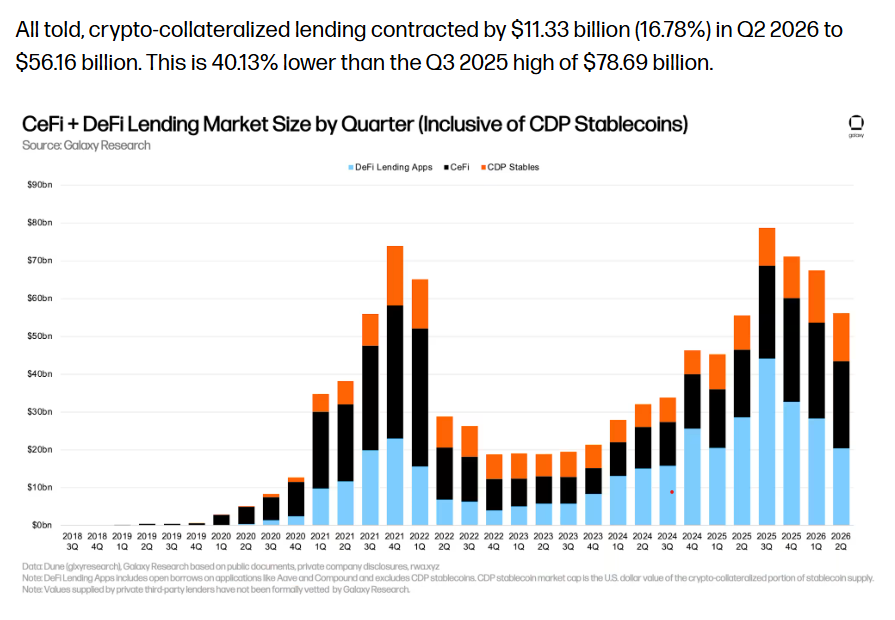
According to figures published by analytics firm Galaxy, an estimated $11.33 billion left the crypto lending sector during the second quarter. This steep contraction was driven in large part by a severe crisis of confidence among lenders and depositors. The catalyst for the downturn arrived in April, when a high-profile exploit struck the Kelp DAO protocol. The security breach left users of Aave, widely regarded as one of the most trusted protocols in the decentralized finance ecosystem, entirely unable to access their Ethereum holdings.
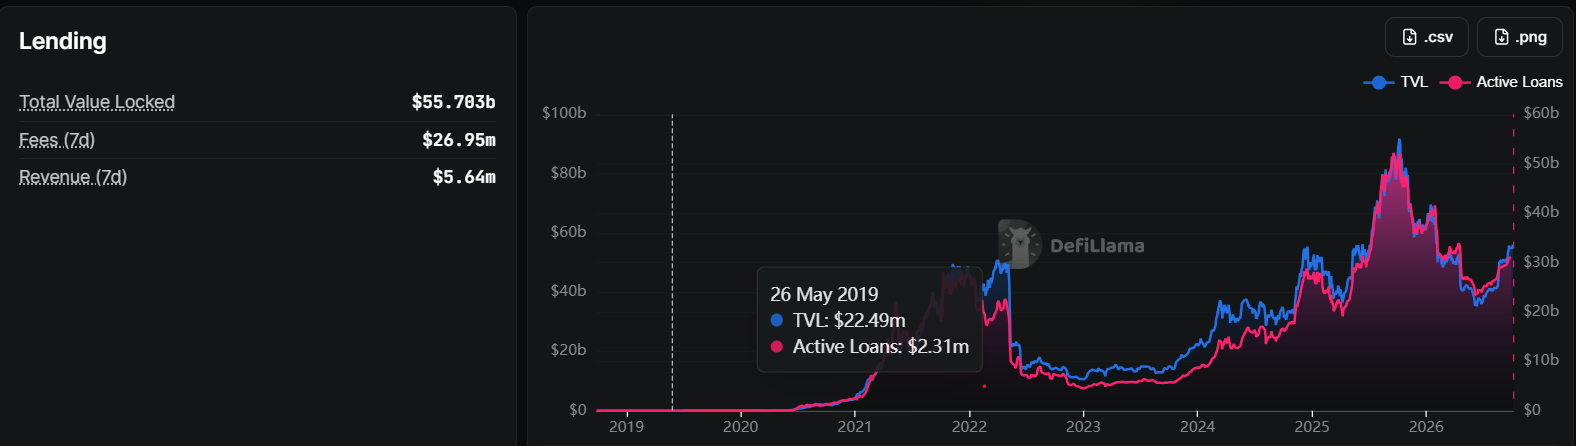
Since the beginning of July, however, the tide has turned dramatically. The total value locked within crypto lending protocols has surged by more than 55%, climbing from its quarterly lows to sit comfortably around $56 billion today, according to data from DeFiLlama.
Yet this rapid recovery brings a familiar challenge into sharp focus: as the total value locked expands, the honeypot grows larger and more attractive to malicious actors. This raises a fundamental question for the modern digital asset economy. Can users truly trust interlinked DeFi lending protocols in an era defined by AI-assisted hacks? In today’s highly composable ecosystem, an exploit originating from any single protocol can trigger a cascading series of devastating effects for all other protocols connected to it through shared liquidity, bridges, or collateral frameworks.
Stani Kulechov, founder and chief executive of Aave Labs, notes that systemic risk management has quickly become a top priority for the industry. When discussing how modern lending markets interact with external assets, Kulechov points out that a protocol’s risk profile extends far beyond its own smart contracts.
"When a protocol accepts a token as collateral, it is also accepting that token’s bridge, its verifier configuration, its oracle and its issuer’s operational security," Kulechov explains.
That holistic vulnerability is precisely what landed Aave in unexpected trouble earlier in the year, highlighting the complex web of dependencies that underpins modern decentralized finance.
An Expanding Attack Surface
The vulnerabilities of a highly interconnected ecosystem became glaringly obvious in April when hackers successfully exploited a Kelp DAO cross-chain route. The attackers managed to mint 116,500 unbacked restaked Ethereum tokens, known as rsETH, which had an approximate market value of $290 million at the time of the exploit. Many of these fraudulent tokens were swiftly deposited as collateral across various Aave markets to borrow other high-value digital assets.
Even though Aave’s own core smart contracts were never directly breached or compromised during the incident, the psychological impact on the broader market was immediate and severe. The protocol experienced a staggering drop in deposits, shedding roughly $15 billion in the days immediately following the exploit. To protect remaining users and maintain solvency, Aave was forced to emergency-freeze its rsETH and wrapped rsETH (wrsETH) markets.
Reflecting on the crisis, Kulechov explains that Aave has since overhauled its security framework to adopt a much broader, more comprehensive perspective.
"We rebuilt our approach around that wider view," Kulechov says. "Our starting point is that security can’t stop at the smart contract."
He adds that traditional security audits and code reviews historically missed the systemic risk sitting quietly in the underlying bridges, verifier networks, and external infrastructure that a single wrapped asset relies upon.
For ordinary users and institutional participants alike, navigating the decentralized lending landscape will increasingly require a careful, critical judgment of how exposed any given protocol is to both internal and external systemic risks.
"Every wrapper, bridge and oracle between the lender and the underlying asset is another place a loan can go wrong," says Thomas Wu, chief financial officer of Bitcoin-backed lending platform Ledn.
Similarly, Sid Powell, co-founder and chief executive of crypto credit platform Maple, emphasizes that serious lenders must operate on the fundamental assumption that a borrower can fail at any given moment, forcing risk managers to work backward from that worst-case scenario.
"What am I holding, where is it, can I see it in real time, and how quickly can I get to it if something breaks?" Powell asks, outlining the core questions that modern credit managers must constantly address.
When Security Fails, Containment Matters
Addressing these systemic vulnerabilities requires a fundamental shift in how protocols evaluate collateral and risk. Sam MacPherson, chief executive of decentralized lender Spark, explains that his team goes far beyond standard smart contract audits. They regularly review governance design, operational security standards, collateral quality, liquidity management practices, and dependencies spread across the wider digital asset ecosystem.
In fact, Spark’s risk management team had already begun phasing out rsETH on SparkLend back in January—months before the April Kelp exploit materialized. That decision was made after a rigorous internal assessment concluded that the asset’s low usage and minimal protocol revenue simply did not justify the additional risk introduced by supporting it.
Kulechov notes that Aave has introduced similar proactive mechanisms, establishing a policy where every listed asset is re-reviewed on a quarterly basis, as well as immediately following any material market change. According to Kulechov, the protocol has already initiated an orderly wind-down process for assets across six different blockchain networks that failed to meet updated chain-level security standards.
"No protocol can control the entire ecosystem, but it can control how much of that risk it takes on and how quickly it responds," Kulechov points out.
While preventing failures entirely remains the ultimate objective, MacPherson stresses that protocols must also have robust, tested procedures in place to respond swiftly if an unexpected breach does occur.
"Preventing losses is only part of the challenge," MacPherson says. "Protocols also need to demonstrate how a loss would be contained if something does go wrong."
The Margin for Human Error
Beyond code vulnerabilities and bridge exploits, industry leaders point out that human error remains one of the most significant yet frequently overlooked risks in the crypto lending space. Shawn Owen, founder and chief executive of SALT Lending, highlights that many of the most damaging financial losses in the history of the sector have stemmed from basic administrative failures rather than complex algorithmic exploits.
"A lot of the biggest losses have come down to key management, access controls or someone getting socially engineered, and a smart contract audit won’t catch any of that," Owen notes.
Additional structural risks inevitably materialize when digital asset lenders deploy customer funds elsewhere to generate high yields. The broader crypto lending industry learned this hard lesson during the brutal market unwind of 2022, when major centralized lenders such as Celsius, Voyager, and BlockFi suffered catastrophic collapses after taking on speculative risks that their customers either did not understand or never expected them to take.
To minimize this attack surface and protect user deposits, platforms like Ledn take a radically conservative approach, choosing to keep client Bitcoin with qualified institutional custodians rather than actively lending it out into risky secondary markets to chase fleeting yield opportunities.
Wu explains that every secondary transaction represents an additional point of potential failure, meaning that fewer operational movements directly correlate to a lower risk profile.
"The only way to take those risks off the table is to keep client Bitcoin in segregated custody, with tight controls and as few movements as possible," Wu says.
Powell warns of a recurring psychological trap in the lending market: when customer deposits start flowing into a platform faster than managers can find safe, high-quality places to deploy capital, the intense commercial pressure to maintain attractive yields can easily lead to poor decision-making.
"So they take on a little more risk to get there. Maybe the collateral standards get looser, or they lend to a borrower they’d have turned down a year ago," Powell explains. "The managers who hold up in a downturn are usually the ones who were willing to say no to capital when they didn’t have a good place to put it."
Can AI Make Lending Safer?
Amid growing discussions surrounding AI-assisted hacks, sophisticated cyber exploits, and autonomous software agents escaping human control, artificial intelligence is simultaneously emerging as a powerful tool to help make crypto lending infrastructure safer.
Aave has already begun incorporating AI-assisted testing alongside its conventional security auditing processes. The protocol recently utilized mutation testing to deliberately inject hundreds of artificial bugs into its V4 smart contract codebases. Remarkably, its automated AI test suites successfully caught 271 out of 304 injected vulnerabilities.
In a recent comprehensive security review of its V3 and V4 codebases, three distinct AI security tools generated a combined 71 findings. Following rigorous manual reviews by human security experts, 20 of those findings were confirmed to be genuinely valid issues. The remaining 51 findings highlighted why human security professionals will likely remain indispensable to the industry for the foreseeable future.
"AI is very good at breadth and speed," Kulechov observes, "but around 70% of the raw findings were false positives, so expert judgment stays essential."
At the same time, artificial intelligence represents a complex double-edged sword for the industry. As autonomous AI agents increasingly take on the responsibility of managing capital on-chain, their specific permissions, data inputs, and internal decision-making logic inevitably transform into another potential attack surface that must be rigorously secured.
"As AI agents start managing capital onchain, their permissions, inputs and decision logic become things that need to be secured just like a contract," Kulechov concludes.
As the crypto lending market continues its steady recovery toward previous capital peaks, the central challenge facing developers and institutional participants alike is no longer just writing secure smart contracts. It requires ensuring that every interconnected component of the modern financial puzzle is thoroughly understood, continuously monitored, and properly contained when unexpected disruptions occur.
 Jia Lissa
 Layla Zulfa