
 By Neng Nana
Federal Bureau of Investigation agents have arrested the co-founder of a Canadian cybersecurity firm in Pennsylvania, marking a significant escalation in the ongoing, high-stakes international investigation into the notorious ShinyHunters hacking group. The suspect, a prominent figure in the cyber extortion advisory industry, was taken into custody on Thursday following an unfolding series of law enforcement actions that have recently targeted both high-level hackers and intermediaries operating within the ransomware negotiation ecosystem.
The arrest follows a recent, deeply embarrassing breach in which the ShinyHunters group successfully infiltrated FBI systems, relieving the bureau of sensitive data pertaining to thousands of agents, including detailed records on personnel units, specializations, and confidential medical and psychiatric files. Multiple sources close to the ongoing investigation confirmed the details of the arrest to KrebsOnSecurity, shedding light on a fast-moving international crackdown that has centralized its operations within an FBI field office in Texas.
Public confirmation of the arrest initially came via mainstream reports and social media. The New York Times reported that federal authorities had detained a Canadian man in Pennsylvania on suspicion of assisting ShinyHunters. Concurrently, a brief statement posted to Twitter/X by FBI Director Kash Patel acknowledged the apprehension of a suspect, though initial official communications refrained from disclosing the individual’s identity or specific corporate affiliations.
According to sources familiar with the inquiry, the Canadian national traveled to Pennsylvania to attend a prominent cyber insurance and risk conference. The suspect’s professional background centers heavily on specialized advisory work, notably handling complex ransomware negotiations and extortion settlements on behalf of corporate clients facing intense digital coercion.

An online review of industry events points directly to the CyberRisk Summit, which was held at the Loews Philadelphia Hotel. Conference documentation and sponsor listings reveal that while the summit featured numerous industry participants, its largest and most prominent sponsor was a Canadian security firm known as Cypfer. Public professional networking profiles indicate that Cypfer was co-founded by Edward Dubrovsky, a Canadian security professional who later became associated with another participating firm, CyberSteward.
Approximately one month prior to his arrest, Dubrovsky shared plans on professional platforms regarding his attendance at the Philadelphia summit alongside his CyberSteward colleagues. In a public post, he emphasized his ongoing focus on strategies surrounding compliant-driven, coercive extortion advisory services, global negotiations, and impartial settlement solutions.
Federal court records filed in Pennsylvania reveal that an individual named Edward Dobrovsky—noting a slight spelling variation in the last name—was formally arrested on October 8. The defendant faces serious charges including conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges related to the interference of commerce through threats. While several critical documents, including the core criminal complaint, remain sealed by the court, a summary of the charges was indexed on public legal databases such as Courtlistener.com.
Inmate location databases maintained by the U.S. Bureau of Prisons indicate that a 54-year-old individual matching Dubrovsky’s identity is currently detained at a federal facility in Philadelphia. However, court dockets show that a notice was filed immediately following the arrest to transfer the case jurisdiction to the Eastern District of Texas, which sources indicate has become the primary operational epicenter for the comprehensive FBI investigation into the ShinyHunters collective. Representatives for the FBI declined to comment on the ongoing proceedings.
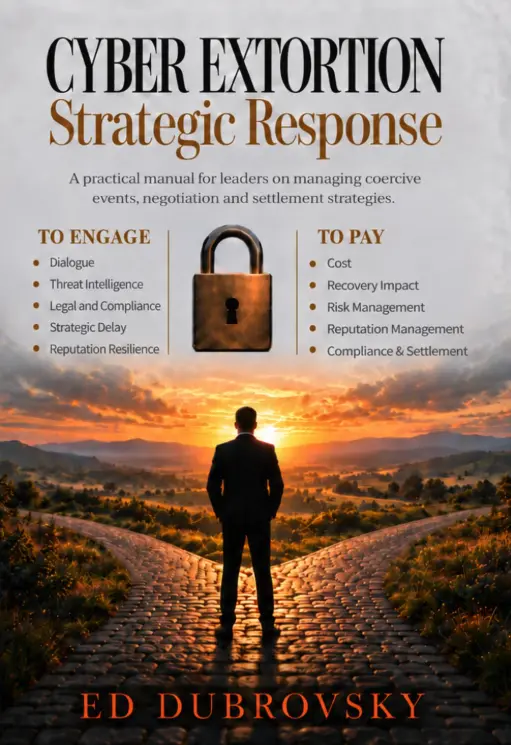
Dubrovsky is also well-known within the cybersecurity publishing space as the author of Cyber Extortion Strategic Response, a 252-page volume marketed as a comprehensive guide designed to navigate organizations past the initial shock of a ransom note and into structured decision-making regarding crisis management, recovery, and risk mitigation. Excerpts from the book’s promotional materials highlight a central tenet of modern incident response: that direct communication with cybercriminals is distinct from negotiating a payment, and that opening channels of engagement does not constitute a commitment to meet extortion demands. Instead, the text argues that structured communication can serve alternative defensive objectives, such as validating threat actor claims, collecting intelligence, stalling for time, and preserving institutional options while leadership evaluates subsequent strategic moves.

At the time of reporting, Dubrovsky could not be reached for direct comment, and inquiries directed to other leadership figures at CyberSteward remained unanswered. Available judicial records indicate that the defendant has not yet retained private counsel, nor has a public defender been formally appointed by the court.
The broader investigation centers on the tactics of the ShinyHunters hacking group, which routinely relies on targeted phishing campaigns and compromised credentials to siphon proprietary data from corporate accounts residing within software-as-a-service providers. Once sensitive databases are exfiltrated, the group typically issues ultimatums demanding substantial financial settlements under the threat of public data leaks. According to federal estimates, the syndicate has successfully extorted more than $70 million from corporate victims throughout the year.
Investigators have been meticulously analyzing digital devices seized last month during an international operation in which Dutch police apprehended Pepijn van der Stap, a convicted cybercriminal linked to the unfolding ShinyHunters conspiracy. Intelligence gathered from these physical and digital seizures has accelerated the pace of the investigation, with federal sources indicating that criminal charges against principals at other firms specializing in ransomware negotiation could be imminent.
The pressure on the hacking collective intensified dramatically following Van der Stap’s arrest. Seizing control of the group’s operations, a faction member operating under the online pseudonym "Rey" began publicly taunting federal authorities over the massive breach of the FBI’s online recruitment portal. This stolen cache exposed highly sensitive administrative data, including unit assignments, specific professional expertise, and confidential medical records belonging to bureau personnel.
Subsequent international reporting revealed that the individual operating as Rey was identified as a teenager named Saif Al-din Khader. Investigative timelines indicate that Khader was tracked down and detained while the cybercrime syndicate was actively attempting to execute an extortion scheme against a digital aviation and navigation unit recently divested by Boeing. Law enforcement officials confirm that Khader is currently cooperating with federal investigators as the sprawling, multi-jurisdictional case continues to develop.
 Nila Kartika Wati
 Sagoh
 Ammar Sabilarrohman