
 By Lina Irawan
Federal Bureau of Investigation agents have arrested a high-profile executive at a Canadian cybersecurity firm in connection with an escalating international investigation into the notorious ShinyHunters hacking collective. The arrest follows a high-stakes cyber intrusion in which the threat group allegedly siphoned sensitive records pertaining to thousands of federal agents from internal bureau systems.
According to multiple sources speaking to KrebsOnSecurity, the suspect was taken into custody in Pennsylvania, where he had been attending a major industry gathering. The high-profile development aligns with reporting from The New York Times, which confirmed that federal authorities had detained a Canadian man in the state on suspicion of providing assistance to the ShinyHunters operation. While neither initial media reports nor a public statement issued on X by FBI Director Kash Patel explicitly named the individual, federal court records and industry sources have identified him as Edward Dubrovsky, a prominent figure in the cyber extortion and incident response sector.
Sources close to the ongoing federal inquiry revealed that Dubrovsky had traveled to Pennsylvania to participate in the Cyber Risk Summit, an annual cyber insurance and risk management conference held at the Loews Philadelphia Hotel between October 5 and October 7. Conference documentation indicates that Dubrovsky was closely tied to CyberSteward, a Canadian security firm and prominent sponsor of the summit. Prior to his tenure with CyberSteward, Dubrovsky was associated with Cypfer, another Canadian security company that served as the primary sponsor for the Philadelphia event.
Federal court records filed in Pennsylvania on October 8 show that an individual named Edward Dobrovsky—with a minor spelling variation in the surname—was formally charged with cyber extortion and conspiracy offenses. Although a significant portion of the judicial docket, including the core criminal complaint, remains under seal, a summary indexed at CourtListener.com sheds light on the preliminary allegations. The court documents charge the defendant with conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges of interference with commerce by threats.

Further verification from the U.S. Bureau of Prisons inmate locator confirmed that a 54-year-old Edward Dubrovsky is currently being detained at a federal detention facility in Philadelphia. However, docket entries filed on October 9 indicate that the legal proceedings have been officially transferred to the U.S. District Court for the Eastern District of Texas. Multiple sources familiar with the trajectory of the federal investigation note that the Texas field office has recently assumed centralized control over the broader multi-jurisdictional case against ShinyHunters. Representatives for the FBI declined to comment on the ongoing litigation.
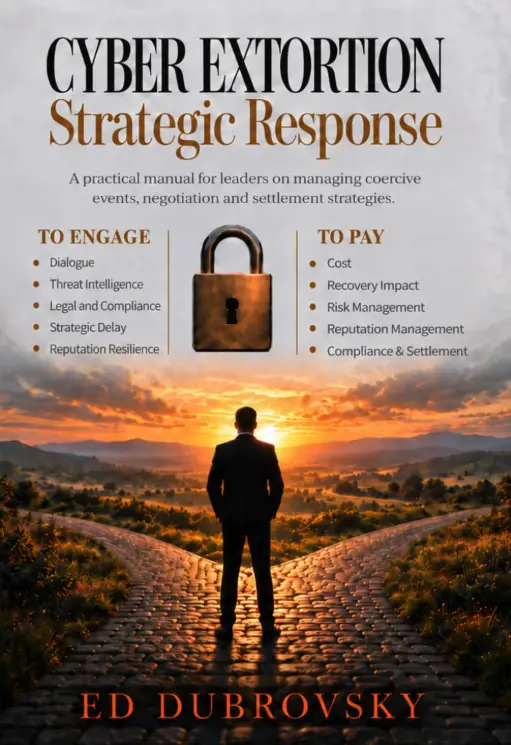
Dubrovsky’s professional background includes authorship of Cyber Extortion Strategic Response, a 252-page volume marketed as an operational manual examining the complexities of ransomware negotiations, incident management, and organizational recovery. Promotional material for the book emphasizes a strategic distinction often debated within the cybersecurity industry: that communicating with malicious actors is distinct from negotiating a payment, and that dialogue does not inherently equal a commitment to yield to extortion demands. The book argues that such engagement can serve alternative defensive objectives, such as validating threat actor claims, collecting intelligence, stalling for time, and maintaining operational options during a crisis.
As of press time, Dubrovsky could not be reached for direct comment, and available court records indicate that he has not yet retained private legal representation or been assigned a public defender by the court.
The ShinyHunters syndicate has long operated as a formidable force in the cybercrime landscape, frequently employing sophisticated phishing campaigns and stolen credentials to infiltrate corporate software-as-a-service environments. Once inside victim networks, the group typically exfiltrates proprietary data and threatens public disclosure unless substantial cryptocurrency ransoms are satisfied. According to FBI estimates, the collective has successfully extorted upward of $70 million from corporate and organizational victims over the course of the year.
The arrest in Pennsylvania represents the latest milestone in a fast-moving international dragnet targeting the infrastructure and associates of ShinyHunters. Investigators have spent weeks analyzing digital devices seized last month during an operation by Dutch law enforcement, which resulted in the arrest of reformed hacker Pepijn van der Stap in connection with the same cybercrime probe. Law enforcement sources suggest that the ongoing scrutiny could soon yield additional criminal charges against principals at other firms specializing in ransomware negotiation and incident advisory services.

The pressure on the hacker collective intensified dramatically following Van der Stap’s arrest. A prominent member of ShinyHunters operating under the online moniker "Rey" assumed leadership of the group and initiated a series of public provocations directed at federal law enforcement. These taunts stemmed from a high-profile breach of the FBI’s online recruitment portal, which exposed sensitive records containing personnel details, unit assignments, professional specializations, and confidential medical and psychiatric histories of prospective and active agents.
Last week, Reuters reported that the individual operating as Rey—subsequently identified as a teenager named Saif Al-din Khader—had been detained by authorities and was actively cooperating with federal investigators. Additional investigative reporting detailed how Khader was apprehended just as the cybercrime group allegedly sought to execute an extortion scheme against a digital aviation and navigation unit recently divested by aerospace giant Boeing.
Federal authorities and cybersecurity researchers anticipate further developments as the investigation continues to unfold across multiple jurisdictions. Additional updates will be provided as court filings and official statements become available.
 Nila Kartika Wati
 Sagoh
 Dwi Wanna