
 By Asep Darmawan
Federal Bureau of Investigation agents have arrested a high-profile executive at a Canadian cybersecurity firm in Pennsylvania, marking a dramatic escalation in the ongoing, high-stakes international investigation into the notorious ShinyHunters hacking collective. The arrest comes on the heels of a devastating cyberattack orchestrated by the group that successfully compromised the FBI’s own systems, making off with sensitive personnel data belonging to thousands of federal agents.
According to multiple sources familiar with the matter, the suspect was taken into custody while visiting Pennsylvania to attend a prominent cyber insurance conference. The individual’s company specializes in navigating complex ransomware negotiations and providing advisory services to corporate victims of cybercrime. The New York Times was first to report the apprehension of a Canadian man in Pennsylvania on suspicion of providing assistance to ShinyHunters, though initial public statements from federal authorities—including a brief post on social media by FBI Director Kash Patel—omitted the suspect’s identity.
Federal court records indicate that an individual named Edward Dobrovsky—with a slight misspelling of the last name—was formally arrested on October 8 on charges of cyber extortion and conspiracy. While a significant portion of the docket, including the core criminal complaint, has been placed under seal by the court, a handful of documents indexed on CourtListener.com shed light on the nature of the allegations. The available summaries charge the defendant with "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats."
An online search of industry events reveals that the Cyber Risk Summit was held at the Loews Philadelphia Hotel from October 5 through October 7. The conference featured numerous sponsors, but according to the summit’s official website, its premier sponsor was a prominent Canadian security firm known as Cypfer. Public professional profiles on LinkedIn indicate that Edward Dubrovsky was previously associated with Cypfer, where his profile claimed he was an ex-founder. Dubrovsky more recently became affiliated with another Canadian security firm and conference sponsor, CyberSteward, and had posted online roughly a month prior to the event expressing his intention to attend the Philadelphia summit alongside his new team.

In the wake of the arrest, representatives for Cypfer clarified Dubrovsky’s corporate history, noting through a company spokesperson that he was never a founder or co-founder of the firm, but rather served as a managing director prior to his resignation in November 2025. In his professional communications, Dubrovsky frequently championed global, agnostic advisory strategies for handling coercive extortion and ransomware settlements, writing on social media ahead of the conference about his focus on continuing conversations surrounding strategy and compliant-driven advisory services.
Federal inmate locator records from the U.S. Bureau of Prisons confirm that a 54-year-old Edward Dubrovsky is currently being held at a federal detention facility in Philadelphia. However, court filings show that the case was officially transferred on October 9 to the U.S. District Court for the Eastern District of Texas. Sources indicate that the Texas field office has become the centralized nerve center for the sprawling, multi-jurisdictional FBI investigation into the ShinyHunters network. The FBI has thus far declined to comment on the specifics of the ongoing case.
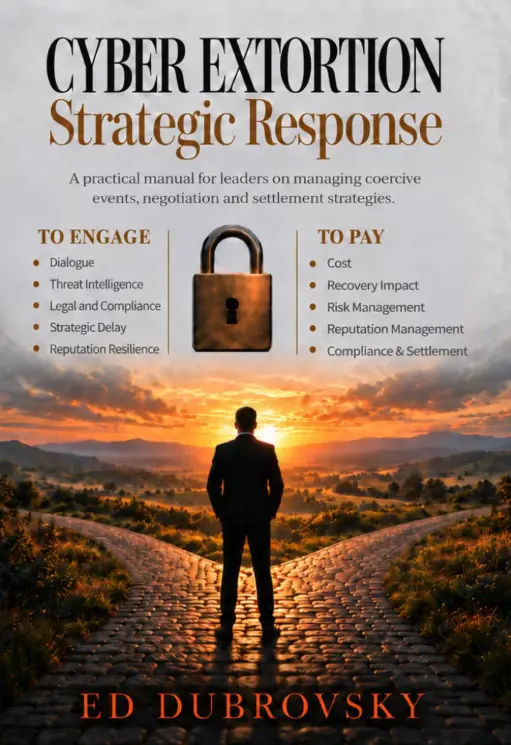
Dubrovsky is also well-known within the cybersecurity publishing space as the author of Cyber Extortion Strategic Response, a 252-page volume focused on the intricacies of handling ransomware incidents. The book’s promotional material emphasizes a core strategic distinction: that communicating with cybercriminals is not synonymous with negotiating a payment, and that entering into dialogue does not commit an organization to meeting a ransom demand. The text outlines how engagement can instead serve alternative defensive objectives, such as testing threat actors’ claims, gathering intelligence, buying valuable time, and preserving options while leadership evaluates its next steps.
At present, court documentation shows that Dubrovsky has not yet retained private legal representation, nor has the court formally appointed a public defender to his case. Attempts to immediately reach Dubrovsky or executive leadership at CyberSteward for comment were unsuccessful.

The ShinyHunters syndicate has long operated by leveraging sophisticated phishing campaigns and stolen credentials to infiltrate corporate accounts across software-as-a-service providers. Once inside, the group extracts proprietary and confidential data, threatening to leak the information publicly unless exorbitant ransom demands are satisfied. According to assessments from federal law enforcement, the hacking collective has successfully extorted more than $70 million from corporate and organizational victims over the course of the year alone.
The dragnet surrounding ShinyHunters has intensified steadily over recent weeks. Sources indicate that FBI investigators have been meticulously combing through digital devices and hardware seized last month by Dutch law enforcement authorities, who apprehended reformed hacker Pepijn van der Stap in connection with the same extortion network. Furthermore, investigators suggest that criminal charges against principals at other firms specializing in ransomware negotiation could potentially be forthcoming as the probe widens.
The pressure on the hacking group reached an unprecedented zenith immediately following Van der Stap’s arrest. A prominent faction leader within ShinyHunters operating under the alias "Rey" assumed operational control of the collective and began brazenly taunting federal law enforcement over a massive security breach. The group had successfully infiltrated the FBI’s own online recruitment portal, exfiltrating sensitive internal records that detailed individual agents’ operational units, professional specializations, and even confidential medical and psychiatric histories.
Law enforcement efforts soon closed in on the digital taunts. Media reports revealed that the individual operating as Rey—identified as a teenager named Saif Al-din Khader—had been successfully detained by authorities and was actively cooperating with federal investigators. The apprehension occurred as the cybercrime group attempted to execute an extortion scheme targeting a navigation and digital aviation unit that had been recently divested by aerospace giant Boeing. As federal authorities continue to follow leads, unravel the group’s financial networks, and examine the intersection of commercial ransomware negotiation and illicit cyber operations, the investigation remains exceptionally active.
 Nila Kartika Wati
 Sagoh
 Dwi Wanna