
 By Pevita Pearce
U.S. federal investigators probing the notorious ShinyHunters hacking group—which recently compromised sensitive data belonging to the Federal Bureau of Investigation—have identified executives at two separate ransomware negotiation firms who maintained unusually close and illicit relationships with the extortion syndicate. According to sources close to the unfolding federal investigation, one of these executives, based in the United States, actively assisted ShinyHunters in operating a dedicated pressure website designed to coerce targeted corporate victims into paying extortion demands.
Cybercriminals aligned with the ShinyHunters banner have claimed responsibility for dozens of high-profile data breaches since the group first emerged in 2019, when operations were primarily run by individuals residing in France. As those founding members were systematically identified, arrested, and jailed by international law enforcement, control over the ShinyHunters operation eventually transitioned to a young cybercriminal known online as "Rey." Last year, investigators identified Rey as a teenage hacker operating out of Amman, Jordan. According to estimates provided by the FBI, ShinyHunters has successfully extorted more than $70 million from corporate and organizational victims over the course of this year alone.
The group’s brazen activities crossed a critical threshold in late September, when hackers tied to ShinyHunters breached the FBI recruitment portal, fbijobs.gov. In a direct taunt to federal law enforcement, the actors threatened to publish confidential files stolen during the intrusion. The leaked cache reportedly contained sensitive internal information, including medical and psychological records, Social Security numbers, home addresses, and specific organizational details regarding individual employees’ units and specializations.
This unprecedented breach of federal infrastructure prompted the bureau to move with exceptional speed, arresting, detaining, and questioning individuals who maintained any digital communication channels with Rey or other core suspects. On October 3, Reuters reported that Rey had been detained by Jordanian authorities and was actively cooperating with the FBI.
Rey’s rise to administrative control over the hacking collective followed the abrupt capture of one of its alleged senior members. On the evening of September 15, law enforcement officers in the Netherlands executed a high-stakes raid, arresting convicted hacker and primary ShinyHunters suspect Pepijn van der Stap. Dutch police reportedly deployed flash-bang grenades to stun and apprehend Van der Stap while he was actively logged into multiple online accounts.
Sources close to the investigation revealed that authorities successfully intercepted Van der Stap while he was using his Signal instant messaging application. This tactical seizure allowed investigators to instantly access and review recent communications with frequent contacts, including ransomware negotiators located in Canada and the United States.

Multiple knowledgeable sources confirmed to KrebsOnSecurity that Van der Stap’s Signal message archives served as the pivotal breakthrough needed to unravel a deeply disturbing murder-for-hire plot that surfaced immediately following his arrest. Dutch media outlet RTL reported last month that two targeted murders were allegedly scheduled to be executed abroad, with investigators finding strong indications that Van der Stap issued the orders for the planned attacks, though no evidence suggests those directives were ever successfully carried out.
Building upon these digital discoveries, the FBI arrested 54-year-old Canadian cybersecurity executive Edward Dubrovsky on October 9 in connection with the broadening ShinyHunters probe. Dubrovsky, who recently authored a published book on handling corporate cyber extortion that explicitly advised victims to always engage and negotiate with hackers, was formally charged with threatening to disclose stolen data and interfering with interstate commerce through extortion, according to federal court documents. Politico reported that federal prosecutors requested Dubrovsky be held in custody pending trial, and court records associated with his case have been placed under seal.
A source close to the investigation disclosed that Van der Stap’s decrypted Signal chats documented frequent, ongoing conversations between the Dutch hacker, Dubrovsky, and at least one executive at a prominent U.S.-based consulting firm. These conversations allegedly demonstrated that the executives frequently possessed insider knowledge regarding newly breached ShinyHunters victims before the targeted organizations themselves even became aware of the intrusions.
Furthermore, federal investigators uncovered an explosive piece of evidence within the Dutch hacker’s chats: Dubrovsky allegedly knew that ShinyHunters had successfully exfiltrated highly sensitive personnel data from official FBI servers. Despite possessing this critical intelligence, Dubrovsky never alerted the bureau to the security breach prior to ShinyHunters publicly threatening on social media platforms to publish the agency’s deeply personal files.
SHINYWIRE
According to two sources close to the federal probe, FBI investigators believe at least one executive at a major U.S.-based consulting firm played an active, hands-on role in operating the now-defunct ShinyHunters victim extortion portal, known as shinywire[.]com. While investigators have identified the firm—a prestigious organization with a workforce exceeding 1,000 associates—news outlets have withheld naming the company and the specific executive pending formal criminal charges.
The Shinywire website remained active from approximately May 3, 2026, until October 16, hosting profiles for nearly 100 corporate and organizational entities compromised by ShinyHunters. Each listing functioned as a pressure point, urging victim organizations to initiate contact with the cybercrime syndicate to negotiate payment terms. The web pages also displayed verified samples of stolen proprietary files, accompanied by explicit threats that the complete data caches would be disseminated publicly if the victim failed to meet financial demands.

Cached records maintained by monitoring services such as urlscan.io captured numerous extortion pages hosted on the site, including a listing targeting Intuitive Surgical, an American medical technology firm that suffered a network breach in March after an employee fell victim to a targeted phishing email campaign. Under the extortion scheme, victim organizations that refused to engage or negotiate within a strict seven-day window found their stolen data permanently published on the main ShinyHunters victim-shaming blog, which remains accessible solely via the Tor anonymity network.
The legal and professional fallout surrounding these networks has already sparked intense internal conflicts within the cybersecurity industry. In mid-October, The Globe and Mail reported that months prior to his federal arrest, Edward Dubrovsky had filed a civil lawsuit in Ontario alleging he had become collateral damage in an aggressive campaign by a former business partner seeking to ruin another industry leader.
Court filings indicated Dubrovsky sued Daniel Tobok, the former chief executive officer of Cypfer, a prominent cybersecurity firm founded in Toronto with international offices spanning the United States, Britain, the Netherlands, the United Arab Emirates, and Mexico. Dubrovsky and Tobok initially partnered in 2017 to build Cypfer, where Dubrovsky served as a managing partner and chief operating officer. However, their relationship deteriorated by 2024, with Dubrovsky alleging that Tobok gradually pushed him out of critical business operations and implemented increasingly erratic administrative decisions.
Tobok denied the allegations, filing a counterclaim accusing Dubrovsky of misappropriating confidential company information and engaging in unfair competition through a separate entity named CyberSteward Inc. Tobok’s filings also asserted that Dubrovsky had mischaracterized his status as a foundational co-owner of Cypfer and held no equity shares.
GHOSTBYTE
Interviews with several former colleagues of Daniel Tobok revealed that as far back as eight years ago, he was recognized within ransomware circles by a distinct moniker: "Ghostbyte." In 2018, a Canadian company fell victim to a cyberattack executed by Dharma, a prolific Russian-language ransomware affiliate operation that emerged in 2016. When the victim company informed the Dharma representative that they were considering paying the ransom due to unrecoverable encrypted files, they requested assurances that the cybercriminals would honor their word upon payment.
A redacted copy of the Dharma representative’s email reply directed the victim to contact an individual at a Canadian IT firm specializing in facilitating such arrangements, explicitly recommending an email address reading [email protected]. The hacker wrote in the response that the IT company frequently resolved similar incidents in Canada and suggested entering a formal service contract, noting that a payment would still be required.

While it remains unverified whether Tobok personally utilized the Ghostbyte address provided by the Dharma affiliate, digital footprint analysis conducted by breach tracking firm Constella Intelligence revealed that an email address frequently used by Tobok—[email protected]—was linked to multiple online accounts utilizing the exact username "ghostbyte," including a Snapchat profile. Furthermore, Constella established a digital connection between the Dharma representative’s email address, [email protected], and a specific cryptocurrency wallet address that processed 38 separate transactions totaling approximately 43 bitcoin, valued at roughly $3.5 million based on contemporary exchange rates.
In a formal public statement issued in mid-October, Cypfer maintained that its corporate operations do not encompass making or facilitating ransomware payments. The company stated that it learned of Dubrovsky’s arrest exclusively through media reports, emphasizing that it had received no outreach from law enforcement and was not the target of any active government investigation.
The statement further clarified that Cypfer and CyberSteward operate as entirely distinct corporate entities sharing no overlapping officers, directors, or employees. Cypfer itself was recently acquired by the Apros Group, a holding company headed by Jason Hogg, a former FBI special agent and former CEO of Aon Cyber Solutions Group. Aon previously acquired Cytelligence in 2020, a security consulting firm where Tobok served as founder and CEO and Dubrovsky operated as managing partner.
CONFLICTING INTERESTS
Under United States law, paying a ransom to obtain an encryption key or secure a promise from cybercriminals to delete stolen data is not inherently illegal. Legal liabilities primarily arise if a victim organization disburses funds to a threat group actively sanctioned by the U.S. Department of the Treasury. Because ShinyHunters does not currently appear on any government sanctions lists, corporate payments to the group do not inherently violate federal sanctions laws.
Industry experts note that ransomware victims are frequently guided by cyber insurance providers toward specific incident response firms. However, specialized forensics and breach response providers maintain vastly differing policies regarding ransom facilitation. While some firms refuse to broker payments to criminal enterprises, companies willing to accommodate such transactions frequently step in once victims decide to pay.
A prominent example occurred in December 2024, when ShinyHunters targeted educational technology provider PowerSchool, exfiltrating private data belonging to 62 million students and 9.5 million teachers across the United States and Canada. PowerSchool reportedly paid a $2.85 million ransom demand, with breach disclosure documentation indicating the company received assistance from CyberSteward. (A ShinyHunters affiliate, 20-year-old Matthew Lane of Sterling, Massachusetts, was subsequently sentenced in November 2025 to four years in federal prison for his acknowledged role in the PowerSchool intrusion.)

Despite the multi-million-dollar payout, the resolution failed to stem subsequent extortion campaigns utilizing the identical stolen dataset. By May 2025, individual school districts began receiving independent ransom demands accompanied by samples of the leaked records. Although investigators have not accused ShinyHunters of orchestrating the secondary extortion wave, the incident underscores a fundamental reality of modern cyber extortion: no technical mechanism exists to verify whether threat actors have permanently deleted stolen files, nor can victims prevent third parties from exploiting compromised records.
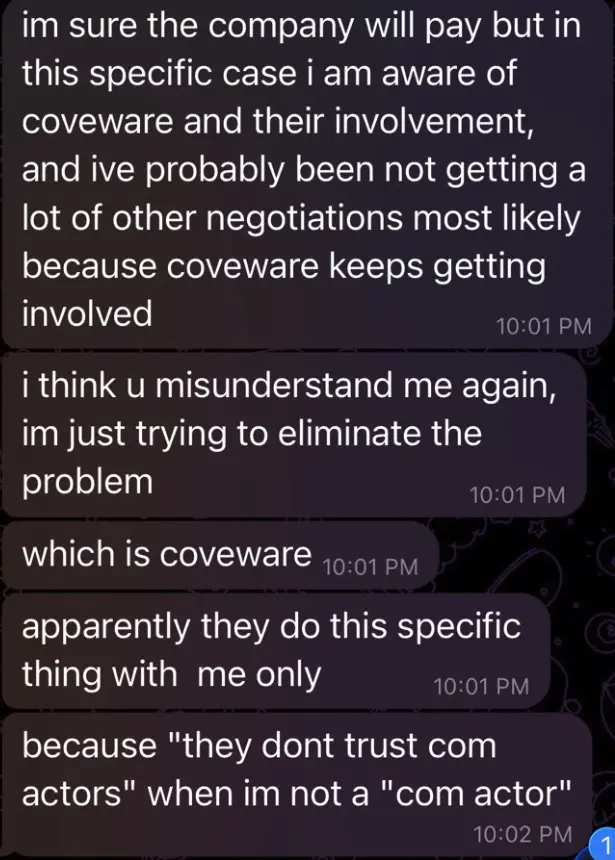
Several leading incident response and intelligence firms, including Coveware and Unit 221B, have consistently advised corporate victims against paying ransoms to ShinyHunters, warning that supposedly destroyed data is routinely retained, resold, or leveraged to directly target corporate clients. The FBI reinforced this guidance in an advisory published on May 15, formally warning organizations against yielding to ShinyHunters’ extortion demands.
Internal communications reviewed by federal investigators illustrate the intense friction generated by these warnings. In private Telegram chats documented in May 2026, leaders of the ShinyHunters collective expressed mounting frustration, explicitly complaining that Coveware’s public advice was severely depressing their ransom collection rates. In one message to a co-conspirator, the main ShinyHunters account lamented that the majority of victim companies would have paid had it not been for Coveware’s guidance, adding that the group was actively seeking to "eliminate the problem."
Mark Camillo, chief executive officer of CyberAcuView—an industry association established in 2021 by major cyber insurance carriers—pointed out that fee structures within the incident response sector create inherent conflicts of interest. While some firms operate on flat-fee retainers, others specializing in ransom negotiation charge a percentage of the total financial payout.
Camillo explained that percentage-based models provide negotiators with a clear financial incentive to advocate for higher ransom payments and discourage aggressive bargaining to reduce settlement figures. Noting that the practice has drawn increasing industry scrutiny, Camillo emphasized that greater transparency is urgently required to eliminate misaligned financial incentives across the cyber defense ecosystem.
Federal prosecutors have increasingly targeted corrupt intermediaries within the ransomware economy. On October 7, the Department of Justice charged MonsterCloud CEO Zohar Pinhasi with wire fraud and conspiracy, alleging he charged corporate clients millions of dollars for technical remediation while secretly paying hackers behind his clients’ backs. Similarly, in July, Florida ransomware negotiator Angelo Martino was sentenced to 70 months in prison for conspiring with the BlackCat/ALPHV ransomware group to extort corporate victims by secretly funneling confidential negotiation strategies to the attackers to maximize extortion payouts.
 Asro
 Nila Kartika Wati
 Sagoh