
 By Basiran
The international cybersecurity landscape has been rocked by the activities of ShinyHunters, a threat group that has claimed responsibility for dozens of major corporate and institutional data breaches since 2019. Originally operated primarily by cybercriminals based in France, the collective underwent significant leadership changes as law enforcement systematically arrested or jailed its early core members. Control of the brand eventually transitioned to an administrator known as "Rey," who was publicly identified last year as a teenage hacker residing in Amman, Jordan. According to FBI estimates, the group has successfully extorted more than $70 million from corporate and governmental victims so far this year alone.
The group’s brazen campaign crossed a critical line in late September when hackers aligned with ShinyHunters breached the official FBI recruitment portal, fbijobs.gov. The attackers taunted federal authorities by threatening to publish a cache of stolen internal files. Reports indicate the compromised material included deeply sensitive personnel information, such as medical and psychological records, Social Security numbers, home addresses, and specific details regarding the unit assignments and specializations of bureau employees.
This high-profile breach of a federal law enforcement portal prompted the FBI to mobilize with exceptional speed, moving to arrest, detain, and question individuals who maintained communication channels with Rey or other suspects linked to ShinyHunters. On October 3, Reuters reported that Rey had been detained by authorities in Jordan and was actively cooperating with federal investigators.
Rey’s consolidation of power over the hacking syndicate followed the swift disruption of a senior co-conspirator. On the evening of September 15, 2026, law enforcement officers in the Netherlands executed a dramatic raid, arresting convicted hacker and ShinyHunters suspect Pepijn van der Stap. Dutch police reportedly deployed flash-bang grenades to stun and apprehend Van der Stap while he remained actively logged into multiple online accounts.

Sources close to the investigation revealed that authorities successfully seized control of Van der Stap while he was actively using his Signal instant messaging application. This immediate intervention granted investigators direct access to his recent communications history, exposing an extensive network of frequent contacts that included professional ransomware negotiators based in both Canada and the United States.
Multiple sources with direct knowledge of the case disclosed that Van der Stap’s decrypted Signal messages provided the breakthrough needed to unravel a disturbing murder-for-hire plot that surfaced immediately following his arrest. Last month, Dutch news outlet RTL reported that two murders were allegedly planned to be carried out abroad, with investigators uncovering indications that Van der Stap had issued the orders for the attacks, though there is no evidence to suggest those violent directives were ever executed.
The widening dragnet soon ensnared prominent figures within the cyber extortion response industry. On October 9, federal authorities arrested Edward Dubrovsky, a 54-year-old Canadian cybersecurity executive, in connection with the ongoing ShinyHunters probe. Dubrovsky, who recently authored a published book on handling cyber extortion that explicitly recommended always engaging with hackers, now faces federal charges including threatening to disclose stolen data and interfering with interstate commerce through extortion, according to court documents. Prosecutors have asked that Dubrovsky remain in federal custody pending trial, and court records related to the case have been placed under seal.
Investigators analyzing Van der Stap’s recovered Signal communications discovered that the Dutch hacker engaged in frequent, detailed conversations with Dubrovsky and at least one executive at a large U.S.-based consulting firm. According to sources familiar with the findings, these executives frequently possessed advance knowledge regarding newly compromised ShinyHunters victims before the victim organizations themselves were even aware of the security breaches.
Perhaps most explosive among the federal findings is evidence indicating that Dubrovsky was fully aware ShinyHunters had exfiltrated highly sensitive personnel data from FBI servers. Despite possessing this critical intelligence, Dubrovsky never alerted the bureau to the breach prior to the public threats made by ShinyHunters on social media to publish the agency’s deeply personal files.

SHINYWIRE
As the probe deepened, investigators turned their attention to the technical infrastructure used by the extortionists. Sources close to the investigation revealed that the FBI believes at least one executive at a prominent U.S.-based consulting firm played an active role in operating a now-defunct extortion portal known as shinywire.com. While the U.S. firm and the suspected executives have not yet been formally charged with a crime, investigators note that the company is a prestigious organization employing more than 1,000 associates. Consequently, law enforcement and reporting entities are currently withholding the specific names of the firm and the individuals under scrutiny.
The Shinywire domain remained active from approximately May 3, until October 16, serving as an online directory featuring nearly 100 organizations that had been compromised by ShinyHunters. Each entry on the portal functioned as a direct pressure tactic, urging corporate victims to open communications with the cybercrime syndicate and discuss financial terms for settlement. The pages prominently displayed samples of stolen corporate and personal files, accompanied by explicit warnings that the full data sets would be disseminated publicly if the victimized companies ignored the ransom demands.
Cached records and indexing tools such as urlscan.io documented numerous extortion listings hosted on the site, including demands directed at high-profile targets like Intuitive Surgical, an American medical technology company that suffered a breach earlier in the year following a targeted employee phishing campaign. Under the operating model utilized by the site, victim organizations that refused to engage or negotiate within a strict seven-day window found their proprietary data dumped onto the main ShinyHunters shaming blog, which remains accessible exclusively via the Tor anonymity network.
The legal and professional fallout from these investigations has already triggered intense corporate warfare within the cybersecurity sector. In mid-October, reports detailed legal battles in Canada stemming from a lawsuit filed by Edward Dubrovsky against Daniel Tobok, the former chief executive of Cypfer, a prominent Toronto-founded cybersecurity firm with international operations. The two men originally formed a business partnership in 2017 to build Cypfer, where Dubrovsky served as managing partner and chief operating officer. However, relations deteriorated significantly by 2024, with Dubrovsky alleging in court filings that Tobok systematically pushed him out of business decisions and attempted to "destroy" his professional standing after their falling out. Tobok denied the allegations and filed a counterclaim accusing Dubrovsky of misappropriating confidential information and competing unfairly through a separate entity named CyberSteward Inc.
GHOSTBYTE
Background inquiries into Daniel Tobok revealed further historical connections to the broader cyber extortion ecosystem. Interviews with former colleagues indicate that years prior, Tobok was known within certain ransomware circles by the alias "Ghostbyte." In 2018, a Canadian company targeted by Dharma—a prolific, Russian-language ransomware affiliate program operating since 2016—sought guidance regarding guarantees that the criminal group would honor a decryption promise if paid. In email correspondence obtained from the incident, a Dharma representative advised the victim to contact an external IT professional in Canada, explicitly recommending the email address [email protected] to negotiate terms and establish a service contract.

While it remains unproven whether Tobok actively utilized the Ghostbyte email address, threat intelligence analysis conducted by Constella Intelligence indicates that a primary personal email address frequently used by Tobok is associated with multiple online user accounts operating under the exact username "ghostbyte," including a Snapchat profile. Furthermore, technical analysis linked the Dharma representative’s fallback email address to a cryptocurrency wallet that processed dozens of transactions worth millions of dollars during its active period.
Representatives for Cypfer issued statements emphasizing that the firm’s core business operations do not encompass making or facilitating ransomware payments. Cypfer maintained that it had no prior knowledge of Dubrovsky’s arrest and has received no direct outreach or investigative scrutiny from law enforcement agencies. The company noted that it operates entirely independently of CyberSteward and has undergone recent corporate acquisition by the Apros Group, a holding company led by Jason Hogg, a former FBI special agent and former leader of Aon Cyber Solutions Group. Aon had previously acquired Cytelligence, a security consultancy previously founded and led by Tobok alongside Dubrovsky.
Within the United States, paying ransoms to cybercriminals is not inherently illegal, provided the targeted group has not been officially designated as a sanctioned entity by the U.S. Department of the Treasury. Because ShinyHunters has not appeared on federal sanctions lists, victim companies frequently face difficult decisions dictated largely by their cyber insurance carriers, which often mandate collaboration with specific incident response providers.
However, a deep divide exists within the incident response industry regarding ransom facilitation. While some forensics firms refuse to negotiate or reward extortionists under any circumstances, others specialize in managing payments, creating a volatile commercial environment. This dynamic was starkly illustrated during the massive December 2024 extortion campaign against educational technology provider PowerSchool, which involved the theft of private records concerning millions of students and educators across North America. Although PowerSchool reportedly settled a multimillion-dollar ransom demand with assistance from CyberSteward, subsequent events proved that paying extortionists offers no technical guarantee of data deletion. Months later, individual school districts began receiving separate extortion demands utilizing identical stolen data samples.
Leading incident response organizations, including Coveware and Unit 221B, have consistently warned corporate clients against paying ransom demands to groups like ShinyHunters, pointing out that exfiltrated data is frequently retained, resold, or leveraged to execute secondary attacks against a victim’s downstream clients. The FBI issued formal public guidance echoing these warnings, advising organizations against capitulating to ShinyHunters’ demands.

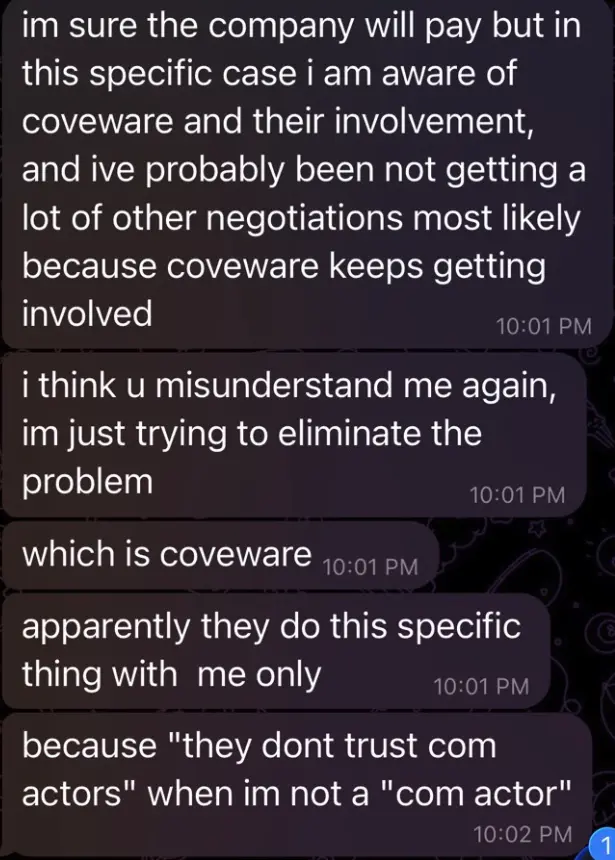
Internal communications recovered by investigators demonstrate the extent to which these anti-ransom advisories disrupted the cybercrime group’s financial operations. Private Telegram chats reviewed by federal sources revealed that the main administrator account for ShinyHunters repeatedly complained that Coveware was actively harming their business model by discouraging victims from paying. In messages exchanged with co-conspirators, the ShinyHunters operator lamented that corporate victims would have complied with ransom demands if not for the counter-advice provided by security firms, leading the group to discuss measures to "eliminate the problem."
Industry leaders have increasingly criticized the structural conflicts of interest inherent in certain ransom negotiation models. Mark Camillo, chief executive of CyberAcuView, pointed out that negotiation firms charging contingency fees calculated as a percentage of the final ransom payment create a perverse financial incentive to maximize payout amounts rather than reduce them.
Federal prosecutors have increasingly targeted these conflicts through criminal indictments. In recent months, the Department of Justice charged multiple ransomware negotiators with wire fraud and conspiracy. These enforcement actions include the prosecution of MonsterCloud CEO Zohar Pinhasi, who was accused of secretly paying cybercriminals millions behind his clients’ backs while inflating remediation bills, and the sentencing of Florida-based negotiator Angelo Martino to prison time for conspiring with the Blackcat ransomware syndicate to maximize victim payouts by leaking confidential negotiation strategies directly to the attackers.
 Reynand Wu
 Dwi Wanna
 Nila Kartika Wati