
 By Raul Delapena Setiawan
U.S. federal investigators probing the prolific cybercrime syndicate known as ShinyHunters have uncovered an alarming nexus between the extortion group and senior executives at prominent ransomware negotiation firms. According to sources close to the ongoing investigation, authorities have identified executives at two separate firms who maintained unusually close and illicit relationships with the cybercriminals. In at least one instance, a U.S.-based executive allegedly assisted the hacking collective in actively operating a specialized website designed to pressure breached organizations into paying exorbitant ransoms.
The revelations come as law enforcement agencies mount an aggressive international crackdown on ShinyHunters, a gang that has claimed responsibility for dozens of major corporate and governmental data breaches since 2019. Originally operated out of France, the collective evolved significantly over the years. As founding members were steadily identified, arrested, and jailed, leadership of the brand eventually gravitated toward a teenage hacker based in Amman, Jordan, known online as “Rey.” Last year, investigators unmasked Rey as the administrative force behind a convergence of notorious threat actor networks, including Scattered Lapsus Hunters. According to recent estimates from the FBI, ShinyHunters has successfully extorted more than $70 million from victims globally this year alone.
The pressure on the group intensified dramatically in late September when hackers aligned with ShinyHunters breached the official recruitment website of the Federal Bureau of Investigation, fbijobs.gov. In a brazen act of digital defiance, the attackers taunted the agency by threatening to publish a trove of highly sensitive stolen files. The compromised data reportedly included confidential medical and psychological records, Social Security numbers, home addresses, and specific details regarding the assignments and specializations of FBI personnel.
The attack on the federal recruitment portal spurred the bureau into swift and decisive action, leading to a wave of detentions and interrogations targeting individuals who maintained digital communications with Rey or other key suspects. On October 3, Reuters reported that Rey had been detained by Jordanian authorities and was actively cooperating with federal investigators.

Rey’s ascent to leadership within the group had been facilitated by the sudden neutralization of a senior co-conspirator weeks earlier. On the evening of September 15, law enforcement officers in the Netherlands executed a high-stakes raid, arresting convicted hacker and ShinyHunters suspect Pepijn van der Stap. Dutch police reportedly deployed flash-bang grenades to stun and apprehend Van der Stap while he was actively logged into multiple online accounts.
According to sources familiar with the operation, authorities seized Van der Stap while he was utilizing the Signal instant messaging application. This tactical breach allowed investigators to immediately review recent communications with his most frequent contacts, including professional ransomware negotiators operating out of Canada and the United States.
Multiple knowledgeable sources indicated that the decryption and analysis of Van der Stap’s Signal messages proved pivotal in unraveling an emerging murder-for-hire plot. Reports from Dutch media outlet RTL last month revealed that two murders were allegedly planned to be carried out abroad, with investigative indications pointing toward Van der Stap as the individual who issued the directives, though there is no evidence the plots were ever executed.
The digital trail soon led directly to the doorstep of the cyber-negotiation industry. On October 9, KrebsOnSecurity broke the news that the FBI had arrested Edward Dubrovsky, a 54-year-old Canadian cybersecurity executive, in connection with the sprawling ShinyHunters investigation. Dubrovsky, who recently authored a book on handling cyber extortion that explicitly advocated for always engaging with hackers, was formally charged with threatening to disclose compromised data and interfering with interstate commerce through extortion. According to court records and reports from Politico, federal prosecutors requested that Dubrovsky remain in custody pending trial while case records were sealed.
Investigators analyzing Van der Stap’s recovered messages discovered that the Dutch suspect maintained routine, extensive conversations with Dubrovsky and at least one executive at a major U.S.-based consulting firm. Troublingly, these communications revealed that the executives frequently possessed detailed knowledge of fresh ShinyHunters victims before the victimized companies themselves had even discovered the breaches.

Perhaps most explosive among the findings shared by investigators was the revelation regarding the FBI data breach. Federal chat logs showed that Dubrovsky was fully aware that ShinyHunters had exfiltrated highly sensitive personnel data from FBI servers long before the group publicly threatened to publish the files on social media, yet he never alerted the bureau to the security lapse.
SHINYWIRE
As the probe widened, investigators unearthed evidence suggesting that at least one executive at a prominent U.S. consulting firm played an active administrative role in operating "shinywire[.]com," a now-defunct extortion portal utilized by ShinyHunters. While law enforcement sources have not yet publicly named the prestigious firm—which employs more than 1,000 associates—or the specific executive involved, the revelation underscores the deepening entanglements between formal remediation services and the extortionists they are hired to fight.
The Shinywire platform remained active from early May until mid-October, cataloging nearly 100 organizations that had fallen victim to ShinyHunters intrusions. Each entry on the site served as a pressure tactic, urging corporate leadership to negotiate payment terms while displaying samples of stolen files alongside threats of total public release if demands were ignored. Among the organizations listed was Intuitive Surgical, a major American medical technology firm compromised in March following a targeted phishing campaign that harvested an employee’s credentials. Under the mechanics of the extortion scheme, victims who failed to engage or reach a settlement within a seven-day window found their complete data portfolios dumped on the group’s Tor-hidden shaming blog.
Legal and industry pressures surrounding the case have already spilled over into civil courts. In mid-October, reports surfaced detailing a bitter legal feud in Ontario between Dubrovsky and his former business partner, Daniel Tobok, the former chief executive of Cypfer. The two had built the Toronto-headquartered cybersecurity firm together after partnering in 2017, with Dubrovsky serving as managing partner and chief operating officer. However, by 2024, their relationship deteriorated amid accusations of exclusion and capricious decision-making. Tobok subsequently filed a counterclaim alleging unfair competition and the misuse of confidential information, setting the stage for deep corporate friction that preceded the current federal indictments.

GHOSTBYTE
The investigation into the broader network of negotiators has also shed light on historical ties between extortionists and figures within the Canadian IT sector. Interviews with former colleagues of Tobok revealed that as far back as eight years ago, he was known to ransomware actors by the moniker "Ghostbyte."
In 2018, a Canadian enterprise fell victim to Dharma, a prolific Russian-language ransomware affiliate program. Seeking assurances that the hackers would honor an agreement to restore locked files and protect stolen data, the victim was advised by a Dharma representative to contact a specific IT professional in Canada. A redacted email exchange provided to investigators showed the ransomware affiliate directing the victim to reach out via the email address [email protected], noting that the individual frequently resolved similar extortion crises in the region.
While it remains unproven whether Tobok actively utilized the Ghostbyte address, digital intelligence firm Constella Intelligence discovered that an email address frequently used by Tobok—[email protected]—was linked to online accounts utilizing the username "ghostbyte," including a Snapchat profile. Furthermore, financial tracing revealed that the Dharma representative’s email address was associated with a cryptocurrency wallet that had processed substantial transactions, underscoring the long-standing financial intersections between ransomware operators and intermediary service providers.
In response to the mounting scrutiny, Cypfer issued a statement clarifying that its business model does not involve facilitating ransom payments and asserting that corporate leadership had no prior knowledge of Dubrovsky’s arrest. The firm emphasized that it has received no outreach from law enforcement and is not the target of any active investigation. Cypfer was recently acquired by the Apros Group, a holding company led by former FBI special agent Jason Hogg. Hogg previously headed Aon Cyber Solutions Group, which in 2020 acquired Cytelligence, a security firm where Tobok served as founder and CEO and Dubrovsky as managing partner.

CONFLICTING INTERESTS
The legal and ethical landscape surrounding ransom payments remains complex. Paying hackers to retrieve decryption keys or secure promises of data deletion is not explicitly illegal under U.S. law, provided the victimized company does not funnel funds to terrorist organizations or groups subjected to strict U.S. Treasury Department sanctions. Because ShinyHunters is not currently designated on federal sanctions lists, victims retain legal latitude in how they respond, though insurance carriers frequently dictate which incident response firms are brought in to handle crises.
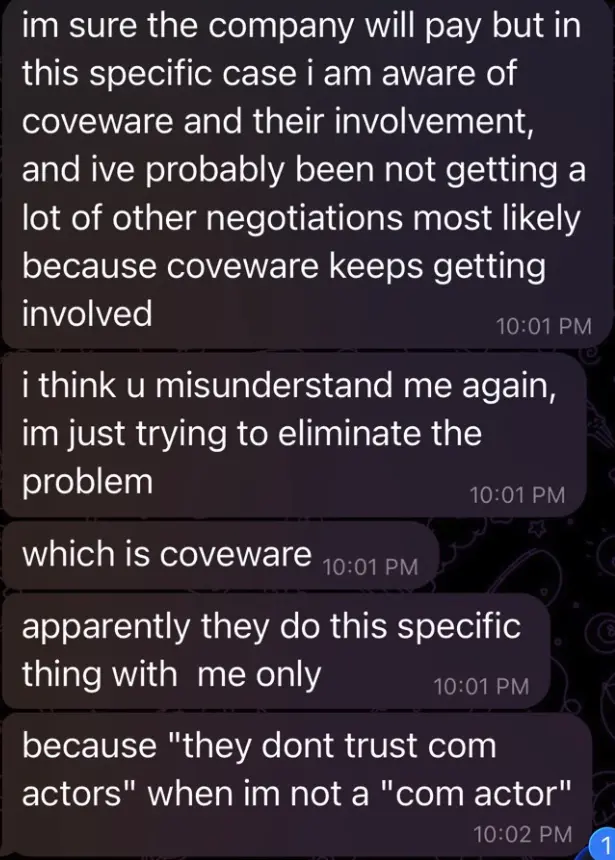
However, the divergence in philosophy among incident response providers has created a volatile marketplace. While firms like Coveware and Unit 221B maintain a strict policy against paying ransoms—warning clients that cybercriminals frequently retain or resell stolen data regardless of agreements—other firms specialize in smoothing the payment process. This divide has frequently placed negotiators in the crosshairs of aggressive threat actors. Internal ShinyHunters chat logs recovered by investigators revealed that group leaders harbored intense animosity toward Coveware, explicitly complaining that the firm’s anti-payment advisories were severely harming their extortion revenue and discussing efforts to "eliminate the problem."
Industry experts point out that the financial structures utilized by certain remediation firms introduce glaring conflicts of interest. Mark Camillo, chief executive of cyber insurance consortium CyberAcuView, noted that firms charging a percentage of the total ransom paid possess an inherent incentive to encourage payouts and maintain high settlement figures. Without greater transparency regarding transaction costs, cryptocurrency float risks, and administrative markups, the ecosystem risks rewarding intermediaries based purely on the volume of extortion currency changing hands.
Recent federal prosecutions highlight the Department of Justice’s intensifying focus on deceptive practices within the remediation sector. In October, federal authorities charged MonsterCloud CEO Zohar Pinhasi with wire fraud and conspiracy, alleging he charged clients millions for remediation while secretly paying hackers behind the scenes. Similarly, in July, Florida ransomware negotiator Angelo Martino was sentenced to nearly six years in prison for conspiring with the Blackcat/ALPHV syndicate to leak confidential client negotiation strategies and maximize victim payouts.
 Asep Darmawan
 Basiran