
 By Ali Ikhwan
A 26-year-old Canadian man once identified as one of the most destructive and consequential cybercrime threat actors of 2024 has officially pleaded guilty to federal charges involving computer fraud and an extensive conspiracy to hack and extort more than 165 major organizations utilizing cloud provider Snowflake. Connor Riley Moucka, a resident of Kitchener, Ontario, also admitted during court proceedings to his involvement in the massive theft of call and text history records belonging to more than 100 million AT&T customers.
According to the U.S. Justice Department, the transnational hacking spree unfolded between February and October 2024. During this period, Moucka and his co-conspirators systematically weaponized stolen login credentials to breach cloud-hosted data environments managed by a prominent U.S.-based software-as-a-service company. The threat actors specifically hunted down credentials associated with Snowflake customer accounts that failed to enforce robust multi-factor authentication policies.
The security lapses exposed sensitive corporate and consumer data across a wide array of high-profile enterprises, leading to targeted extortion and attempted extortion demands against well-known corporations such as TicketMaster, Lending Tree, Advance Auto Parts, and Neiman Marcus. In the wake of the catastrophic data breaches, Snowflake responded by overhauling its security architecture, tightening password complexity mandates, and making multi-factor authentication a mandatory requirement for users.
Throughout his cybercriminal operations, Moucka frequently rotated through a rotating cast of digital aliases, occasionally managing multiple distinct personas simultaneously to mask his activities. However, two of his most prominent online monikers were "Judische" and "Waifu." The direct connection between the alias Judische and the widespread Snowflake data thefts was first brought to light by KrebsOnSecurity in a September 2024 investigation, which explored the murky intersections between Western, English-speaking cybercriminals and extremist groups known for harassing and extorting minors into committing acts of self-harm or violence against others.
That investigative report pinned the identity of Judische on an Ontario-based software engineer who had spent years—dating back to at least 2020—engaging in numerous corporate data breaches and aggressive voice phishing campaigns targeting American entities. Just over a month after the dark nexus was publicly exposed, Canadian law enforcement officials moved in, arresting Moucka on a provisional warrant issued by the United States.
Federal prosecutors outlined the staggering scope of the stolen data, noting that Moucka and his accomplices utilized their unauthorized network access to siphon billions of sensitive consumer records and download terabytes of proprietary information. The compromised data trove included non-content call and text history records, banking and private financial information, employee payroll records, Drug Enforcement Administration (DEA) registration numbers, driver’s license numbers, passport numbers, Social Security numbers, and a wide array of other personally identifiable information. Armed with this sensitive material, the conspirators ruthlessly extorted corporate victims, threatening to leak confidential information onto public forums and dark web marketplaces if ransom demands were not met.
Beyond extorting major corporations, Moucka allegedly directed threats and harassment campaigns at government officials and private security researchers who were actively working to track down his digital footprint. The Justice Department revealed that the criminal enterprise successfully generated more than $2.5 million in extortion payments. In a particularly brazen escalation, Moucka even re-extorted a victim organization by leveraging stolen data belonging to a government officer and the immediate family members of a former government official, threatening further public disclosures if his demands were ignored.
As federal investigators unraveled the conspiracy, additional members of the hacking syndicate began to face legal reckoning. One of Moucka’s co-conspirators, Cameron "Kiberphant0m" Wagenius, a serving U.S. Army soldier, pleaded guilty to charges related to an extortion scheme targeting telecommunications giants AT&T and Verizon for their customer account data. Weeks before Wagenius was taken into custody, independent security journalism deep-dived into his sprawling network of Telegram and Discord accounts, uncovering clues that the operator behind the aliases was actively serving in the military and stationed in South Korea.
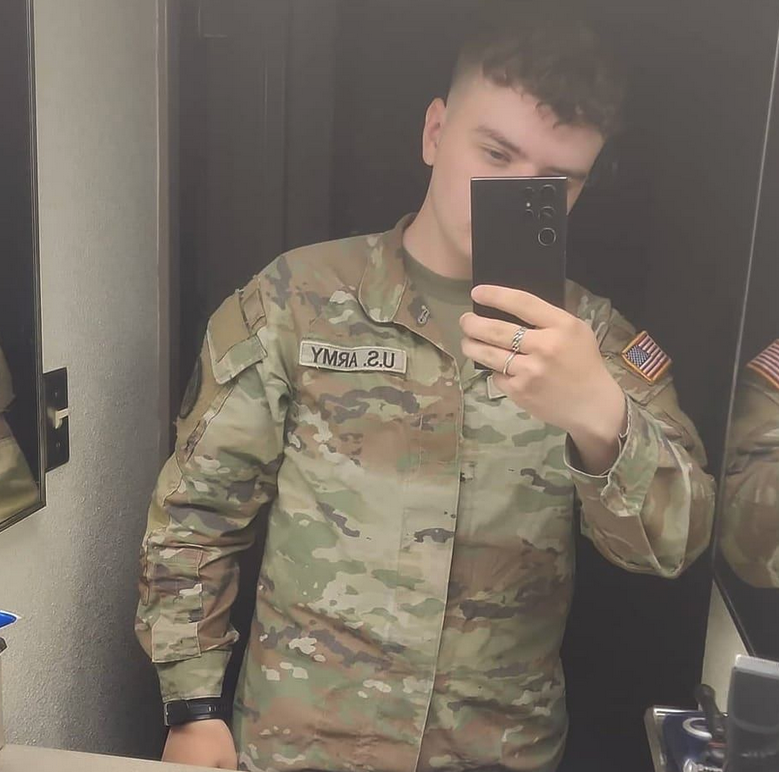
Following Moucka’s apprehension, Wagenius attempted to exert pressure by publishing files on public-facing hacker forums that he claimed were AT&T call logs belonging to then-President-elect Donald Trump and then-Vice President Kamala Harris, alongside engineering schematics allegedly stolen from the U.S. National Security Agency (NSA). Wagenius, who faces substantial prison time including a maximum penalty of 20 years for wire fraud, five years for computer fraud-related extortion, and a mandatory consecutive two-year term for aggravated identity theft, is scheduled to be sentenced in federal court.
Another central figure named in the sweeping investigation is John Erin Binns, a 26-year-old American national who fled the United States after being indicted for his admitted role in a massive 2021 cyberattack against T-Mobile that compromised the personal records of at least 76 million customers. Law enforcement sources close to the case indicated that Binns, who operated under aliases such as "IRDev" and "IntelSecrets," had spent time incarcerated in a Turkish prison before securing his release and quietly re-emerging online. According to those sources, Binns recently acquired Turkish citizenship, a legal status that shields him from foreign extradition under local laws.
For his part in the multi-pronged cybercrime operation, Moucka entered a guilty plea to four distinct criminal counts, encompassing computer fraud, wire fraud, aggravated identity theft, and conspiracy. He is scheduled to face sentencing, where he confronts a mandatory minimum prison sentence of two years for the aggravated identity theft charge, alongside a maximum potential sentence of 30 years for the remaining convictions. The final determination regarding the length of his incarceration will rest with the federal judge presiding over the case, marking the close of a landmark chapter in the prosecution of modern cloud-infrastructure extortionists.
 Nila Kartika Wati
 Sagoh
 Ammar Sabilarrohman