
 By Layla Zulfa
As the broader cryptocurrency market charts flip from red to green, the crypto lending sector has experienced a remarkable resurgence of interest and capital inflow following a particularly dismal second quarter.
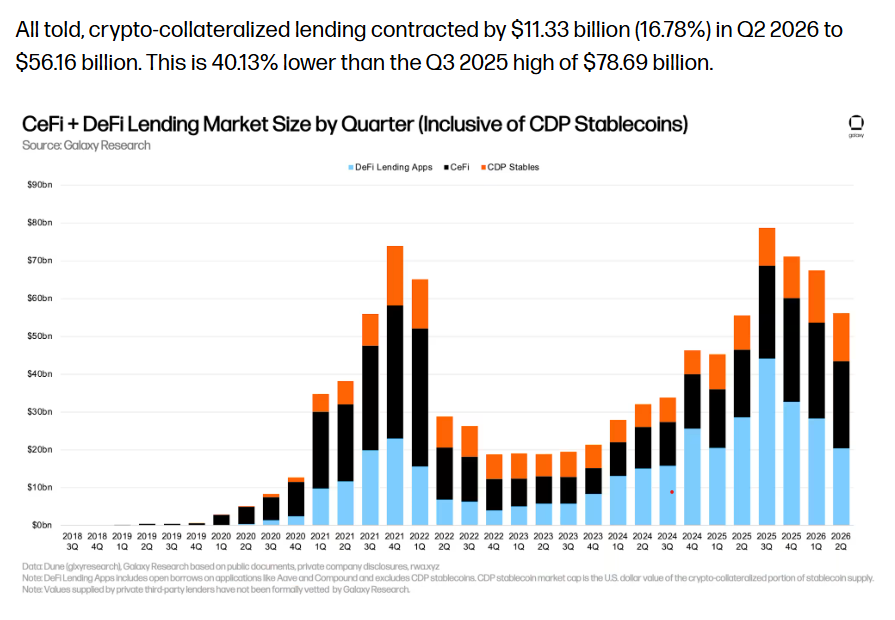
Figures published by Galaxy show that approximately $11.33 billion left the decentralized finance (DeFi) lending sector during Q2. This massive capital flight was partly driven by a spreading crisis of confidence among lenders, which was triggered by the high-profile Kelp DAO hack in April. That exploit left users of Aave, widely regarded as one of the most trusted protocols in the ecosystem, temporarily unable to access their Ethereum holdings.
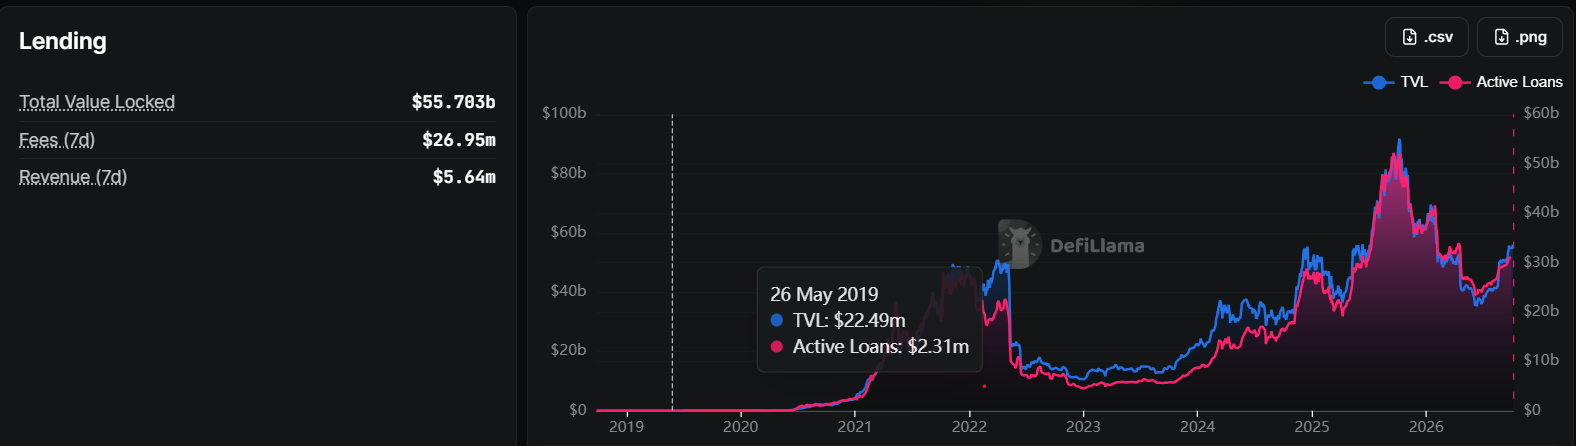
Since the beginning of July, however, the landscape has shifted dramatically. The total value locked (TVL) across DeFi lending protocols has surged by more than 55%, climbing from its quarterly lows to sit comfortably around $56 billion.
Yet, this rapid expansion also means the financial honeypot has grown significantly larger, renewing urgent questions across the industry. Can users truly trust interlinked DeFi lending protocols in the modern era of AI-assisted hacks, where a single exploit in one isolated protocol can trigger a cascade of devastating systemic effects across every other platform connected to it?
Stani Kulechov, the founder and chief executive officer of Aave Labs, notes that this exact systemic vulnerability has now become top of mind for developers and risk managers alike.
"When a protocol accepts a token as collateral, it is also accepting that token’s bridge, its verifier configuration, its oracle and its issuer’s operational security," Kulechov explains.
That interconnected dependency is precisely what dragged Aave into the crosshairs of the spring exploit.
An Expanding Attack Surface
The vulnerabilities of modern multi-chain DeFi were laid bare when hackers successfully exploited a Kelp DAO cross-chain routing mechanism in April. The exploit resulted in the creation of 116,500 unbacked restaked tokens known as rsETH, which had a market value of roughly $290 million at the time. A significant portion of these illicitly minted tokens was subsequently deposited as collateral into various Aave markets to borrow other high-value digital assets.
Even though Aave’s own native smart contracts experienced no direct security breaches or code failures during the incident, the psychological shockwaves hit the protocol hard. Aave saw its total deposits plummet by approximately $15 billion in the immediate aftermath of the exploit. To contain the contagion, the protocol was forced to temporarily freeze its rsETH and wrsETH borrowing and lending markets.
Data compiled by Galaxy illustrates the severity of that prior downturn, highlighting that the broader lending market contracted by 16.78% over the course of the second quarter.
Reflecting on the fallout, Kulechov explains that Aave has since shifted toward a much more holistic approach to security and risk management.
"We rebuilt our approach around that wider view," Kulechov says, emphasizing that traditional security measures are no longer sufficient. "Our starting point is that security can’t stop at the smart contract." He adds that traditional security reviews historically "missed the risk sitting in the bridges, verifier networks and other infrastructure an asset depends on."
For everyday users and institutional participants alike, navigating this complex web requires a sophisticated understanding of how exposed any given protocol is to both internal and external risks.
Thomas Wu, the chief financial officer of Bitcoin-backed lender Ledn, echoes this sentiment regarding multi-layered asset packaging. "Every wrapper, bridge and oracle between the lender and the underlying asset is another place a loan can go wrong," Wu warns.
Sid Powell, the co-founder and chief executive of crypto credit platform Maple, tells industry observers that "serious lenders" should always operate under the assumption that a borrower can fail at any given moment, working backward from that worst-case scenario.
"What am I holding, where is it, can I see it in real time, and how quickly can I get to it if something breaks?" Powell asks, outlining the fundamental questions modern credit managers must address.
When Security Fails, Containment Matters
As the industry attempts to fortify itself against systemic shocks, protocol executives emphasize that robust defense requires looking far beyond basic smart contract audits. Spark, another major DeFi lender, approaches risk by examining the entire operational ecosystem.
Spark Chief Executive Sam MacPherson explains that his team routinely evaluates governance design, operational security practices, underlying collateral quality, liquidity management systems, and dependencies across the broader decentralized finance landscape.
Demonstrating proactive risk mitigation, Spark actually began phasing out rsETH support on its SparkLend platform back in January—months before the April Kelp exploit occurred. The decision was made after internal assessments concluded that the asset’s low usage and minimal revenue generation simply did not justify the additional risk introduced by supporting it.
Kulechov notes that Aave has implemented similarly rigorous mechanisms. Under the protocol’s updated framework, every listed asset is subjected to comprehensive re-reviews on a quarterly basis, as well as mandatory ad-hoc evaluations "after any material change." Kulechov reveals that Aave has already initiated an orderly wind-down process for assets across six different blockchain networks that failed to meet its upgraded chain-level security standards.
"No protocol can control the entire ecosystem, but it can control how much of that risk it takes on and how quickly it responds," Kulechov states.
While preventing failures remains the primary objective, MacPherson stresses that protocols must also maintain meticulous crisis response procedures.
"Preventing losses is only part of the challenge," MacPherson says. "Protocols also need to demonstrate how a loss would be contained if something does go wrong."
The Margin for Human Error
Beyond code vulnerabilities and bridge exploits, industry veterans point out that human error remains one of the single greatest vulnerabilities in digital asset lending—and paradoxically, the one most frequently overlooked by participants.
Shawn Owen, founder and chief executive of SALT Lending, points out that operational oversight often supersedes technical flaws.
"A lot of the biggest losses have come down to key management, access controls or someone getting socially engineered, and a smart contract audit won’t catch any of that," Owen notes.
Additional layers of risk materialize when lenders deploy customer assets into external yield-generating strategies. The crypto lending industry learned this hard lesson during the brutal market deleveraging of 2022, when major centralized lenders including Celsius, Voyager, and BlockFi suffered catastrophic collapses after taking on complex risks that their customer bases neither understood nor anticipated.
To minimize its overall attack surface and eliminate counterparty exposure, Ledn chooses to keep client Bitcoin holdings with qualified institutional custodians rather than actively deploying them into DeFi protocols to generate supplemental yield.
Wu explains that every secondary transaction represents an additional point of potential failure. "So the fewer there are, the lower the risk of a breach," he says. "The only way to take those risks off the table is to keep client Bitcoin in segregated custody, with tight controls and as few movements as possible."
At the same time, market pressures can easily tempt credit managers to compromise their standards. Powell warns that when capital deposits flow into a platform faster than managers can identify safe, productive lending opportunities, the intense pressure to maintain competitive yields can prompt poor decision-making.
"So they take on a little more risk to get there," Powell explains. "Maybe the collateral standards get looser, or they lend to a borrower they’d have turned down a year ago. […] The managers who hold up in a downturn are usually the ones who were willing to say no to capital when they didn’t have a good place to put it."
Can AI Make Lending Safer?
Amid ongoing headlines concerning sophisticated artificial intelligence hacks, automated exploits, and experimental agents pushing boundaries, the technology itself may paradoxically hold the key to making crypto lending significantly safer.
Aave is already integrating AI-assisted testing alongside its conventional security audits. During recent testing phases, the protocol utilized mutation testing to deliberately inject hundreds of artificial bugs into its upcoming V4 smart contract codebases. Impressively, Aave’s AI-driven test suites successfully caught 271 out of the 304 deliberately introduced vulnerabilities.
In a comprehensive review of its V3 and V4 codebases, three distinct AI security tools generated a combined total of 71 findings. Following rigorous manual reviews by human engineers, 20 of those findings were validated as genuine code issues. The remaining 51 false positives, however, underscored the reality that human security experts and developers will likely remain essential to the development lifecycle for the foreseeable future.
"AI is very good at breadth and speed," Kulechov observes, "but around 70% of the raw findings were false positives, so expert judgment stays essential."
At the same time, artificial intelligence remains a distinct double-edged sword for the industry. As autonomous AI agents increasingly take on the responsibility of managing capital directly on-chain, their specific permissions, data inputs, and underlying decision logic inevitably transform into new attack surfaces that must be heavily secured.
"As AI agents start managing capital onchain," Kulechov concludes, "their permissions, inputs and decision logic become things that need to be secured just like a contract."
As the crypto lending market embarks on its latest recovery phase, the overarching challenge for developers, institutions, and users alike is no longer just writing secure code. It requires ensuring that every interconnected component of the modern financial puzzle is thoroughly understood, continuously monitored, and reliably contained the moment something unexpected goes wrong.
 Jia Lissa