
 By rifanmuazin
U.S. federal investigators pursuing the notorious ShinyHunters hacking group—which recently compromised highly sensitive data belonging to the Federal Bureau of Investigation—have identified executives at two separate ransomware negotiation firms who maintained unusually close relationships with the extortion syndicate. Sources close to the ongoing investigation revealed that one of the executives, operating within the United States, actively assisted ShinyHunters in running a dedicated website designed to pressure breach victims into paying ransom demands.
Hackers aligned with the ShinyHunters banner have claimed responsibility for dozens of major corporate and institutional data breaches since 2019. During its initial years, the group was primarily operated by cybercriminals residing in France. As those founding members were systematically arrested, prosecuted, and jailed, operational control over the ShinyHunters brand eventually transitioned to an administrator known as "Rey," who was identified last year as a teenage hacker based in Amman, Jordan. According to estimates provided by the FBI, ShinyHunters has successfully extorted more than $70 million from corporate and public-sector victims so far this year.
The group’s activities reached a critical threshold in late September, when hackers tied to ShinyHunters successfully breached the FBI recruitment portal, fbijobs.gov. The attackers taunted federal authorities by threatening to publish a cache of stolen internal files. Reports indicate the compromised data included sensitive medical and psychological records, Social Security numbers, home addresses, and specific details regarding individual employees’ units and professional specializations.
This brazen breach of a federal law enforcement infrastructure prompted the agency to move with uncommon speed, detaining and questioning individuals who had maintained any form of communication with Rey or other suspects linked to the ShinyHunters network. On October 3, Reuters reported that Rey had been apprehended by Jordanian authorities and was actively cooperating with the FBI.
Rey’s ascent to administrative control over the hacking collective occurred because a key senior member had been abruptly neutralized by law enforcement. On the evening of September 15, 2026, Dutch authorities executed a high-profile raid, arresting convicted hacker and ShinyHunters suspect Pepijn van der Stap. According to accounts from the scene, Dutch police utilized flash-bang grenades to stun and apprehend Van der Stap while he was actively logged into multiple online accounts.
A source close to the investigation disclosed that authorities arrested Van der Stap while he was using his Signal instant messaging application. This immediate physical intervention allowed investigators to access and preserve recent communications with frequent contacts, including professional ransomware negotiators based in Canada and the United States.

Multiple sources with direct knowledge of the matter informed KrebsOnSecurity that Van der Stap’s recovered Signal messages proved instrumental in unraveling a separate murder-for-hire plot that surfaced immediately following his arrest. Dutch news outlet RTL reported last month that two planned murders were allegedly slated to be executed abroad, with investigators finding strong indications that Van der Stap issued the orders for the attacks, though there is no evidence to suggest those violent directives were ever carried out.
On October 9, KrebsOnSecurity broke the news that the FBI had arrested a 54-year-old Canadian cybersecurity executive named Edward Dubrovsky in connection with the broader ShinyHunters investigation. Dubrovsky, who recently published a book on handling cyber extortion that advised victims to always engage with threat actors, was formally charged with threatening to disclose stolen data and interfering with interstate commerce through extortion, according to court records. Politico reported that federal prosecutors requested Dubrovsky remain in custody pending trial, and that documentation related to his criminal case has been placed under seal.
A source familiar with the investigation stated that Van der Stap’s encrypted messaging logs demonstrated frequent, direct conversations between the Dutch hacker, Dubrovsky, and at least one executive at a prominent U.S.-based consulting firm. According to the source, these executives frequently possessed intimate details regarding new ShinyHunters victims before the victimized organizations themselves had even discovered the network intrusions.
Perhaps most explosively, federal investigators discovered through Van der Stap’s chats that Dubrovsky was fully aware that ShinyHunters had exfiltrated highly sensitive data from FBI servers. Despite this knowledge, Dubrovsky never alerted the bureau to the security breach prior to ShinyHunters publicizing its threats on social media to release the agency’s deeply personal personnel records.
SHINYWIRE
As the probe expanded, KrebsOnSecurity learned from two sources close to the ShinyHunters investigation that federal agents believe at least one executive at a major U.S. consulting firm played an active, operational role in managing the now-defunct ShinyHunters victim extortion portal, known as "shinywire[.]com." While federal authorities continue to evaluate evidence, KrebsOnSecurity is withholding the names of the U.S. company and the suspected executive because formal criminal charges have not yet been filed, though the enterprise is a prestigious organization employing more than 1,000 associates.
The Shinywire domain was active from approximately May 3, 2026, until October 16, listing nearly 100 organizations that had been compromised by ShinyHunters. Each entry on the platform pressured victim companies to open lines of communication with the cybercrime collective to negotiate extortion payments. The web pages also displayed samples of stolen data, warning that the complete files would be leaked publicly if victims failed to meet ransom demands.

Cached records from urlscan.io illustrate how the portal targeted organizations such as Intuitive Surgical, an American medical technology company that suffered a network intrusion in March 2026 after an employee fell victim to a targeted phishing email attack. Under the group’s operational model, victim organizations that refused to engage or negotiate within a seven-day window found their stolen files published on the primary ShinyHunters shaming blog, which is accessible exclusively through the Tor anonymity network.
The legal and professional fallout surrounding these networks has already sparked intense corporate infighting. In a mid-October report, The Globe and Mail revealed that months prior to his arrest by the FBI, Edward Dubrovsky had filed civil court documents in Ontario alleging he had become collateral damage in a deliberate campaign by a former business partner to destroy another industry leader.
The lawsuit targeted Daniel Tobok, the former chief executive of Cypfer, a prominent cybersecurity firm founded in Toronto with international offices spanning the United States, Britain, the Netherlands, the United Arab Emirates, and Mexico. Dubrovsky and Tobok initially became business partners in 2017 to build Cypfer, where Dubrovsky served as a managing partner and chief operating officer. However, by 2024, the business relationship had deteriorated significantly, with Dubrovsky accusing Tobok of gradually excluding him from corporate governance and making increasingly erratic business decisions.
Tobok vehemently denied the allegations and filed a counter-claim accusing Dubrovsky of misappropriating confidential information and engaging in unfair competition through concurrent work with another entity known as CyberSteward Inc. Tobok also maintained that Dubrovsky had misrepresented his status as a founding member and was not a corporate shareholder.
GHOSTBYTE
Interviews with several former colleagues of Daniel Tobok indicate that as far back as eight years ago, he was known within ransomware circles by a specific moniker: Ghostbyte. In 2018, a Canadian company fell victim to an intrusion orchestrated by Dharma, a prolific Russian-language ransomware affiliate program active since 2016. When the victim company informed the Dharma representative that they were leaning toward paying the ransom because critical files remained permanently locked, they requested firmer guarantees that the hackers would honor their word.
In a redacted email response provided by investigators, the Dharma operative advised the victim to contact an external IT firm in Canada that specialized in resolving such matters, directing them to communicate via the email address [email protected]. The Dharma representative wrote that the IT company routinely handled such situations in Canada and advised the victim to sign a formal service contract, noting they would still ultimately need to pay.

While it remains unconfirmed whether Tobok personally utilized the Ghostbyte address circulated by the Dharma affiliate, and despite Tobok failing to respond to repeated requests for comment, breach intelligence firm Constella Intelligence discovered a clear digital nexus. Constella found that an email address frequently utilized by Tobok—[email protected]—was directly linked to multiple online accounts utilizing the username "ghostbyte," including a Snapchat profile.
Furthermore, Constella established that the Dharma representative’s contact address, [email protected], was associated with a specific cryptocurrency wallet that processed 38 distinct transactions totaling roughly 43 bitcoin, valued at approximately $3.5 million at current market rates, with the most recent transaction recorded in February 2019.
In an official statement released in mid-October, Cypfer maintained that its corporate operations do not involve making or facilitating ransom payments. The company stated that it learned of Dubrovsky’s arrest through media reports and had no prior knowledge of the federal action. A company representative emphasized that Cypfer had received no outreach from law enforcement and was not the target of any ongoing government investigation.
The statement further clarified that Cypfer and CyberSteward operate as completely separate entities with zero overlapping officers, directors, or employees. Cypfer was recently acquired by the Apros Group, a holding company led by Jason Hogg, a former FBI special agent and former chief executive of Aon Cyber Solutions Group. In 2020, Aon had previously acquired Cytelligence, a security consultancy where Tobok served as founder and CEO and Dubrovsky operated as a managing partner.
CONFLICTING INTERESTS
Under U.S. law, paying ransom to cybercriminals in exchange for decryption keys or commitments to delete stolen files is not inherently illegal, provided the targeted group is not designated as a sanctioned entity by the U.S. Department of Treasury. While ShinyHunters is not currently subjected to official government sanctions, the broader ecosystem surrounding incident response and ransom negotiations remains fraught with ethical and financial complications.
Victims of ransomware attacks are frequently directed by cyber insurance providers to retain specialized incident response firms. However, not all forensic companies agree to facilitate extortion payments. When principled firms decline to reward attackers, clients often transition to negotiation firms willing to process payments.

This dynamic was highlighted during the massive ShinyHunters extortion campaign targeting education technology firm PowerSchool, which began in December 2024 and compromised sensitive records pertaining to 62 million students and 9.5 million teachers across the United States and Canada. PowerSchool reportedly paid a $2.85 million ransom with the assistance of CyberSteward, while a 20-year-old ShinyHunters affiliate from Massachusetts was later sentenced to four years in prison for his role in the intrusion.
Despite that ransom payment, the protection proved illusory. By May 2025, individual school districts began receiving independent extortion demands utilizing samples of the exact same stolen data files. While investigators have not accused ShinyHunters of orchestrating the secondary wave of extortion, the incident underscores a fundamental reality of the cybercrime economy: there is no technical mechanism to verify that threat actors have permanently destroyed stolen data, nor any way to prevent malicious actors from repeatedly abusing compromised records.
Leading incident response firms, including Coveware and Unit 221B, have consistently advised corporate victims against paying ransom to groups like ShinyHunters, pointing out that exfiltrated data is routinely retained, resold, or leveraged directly against a company’s customer base. The FBI reinforced this guidance in a May 2026 public service announcement cautioning against payments.
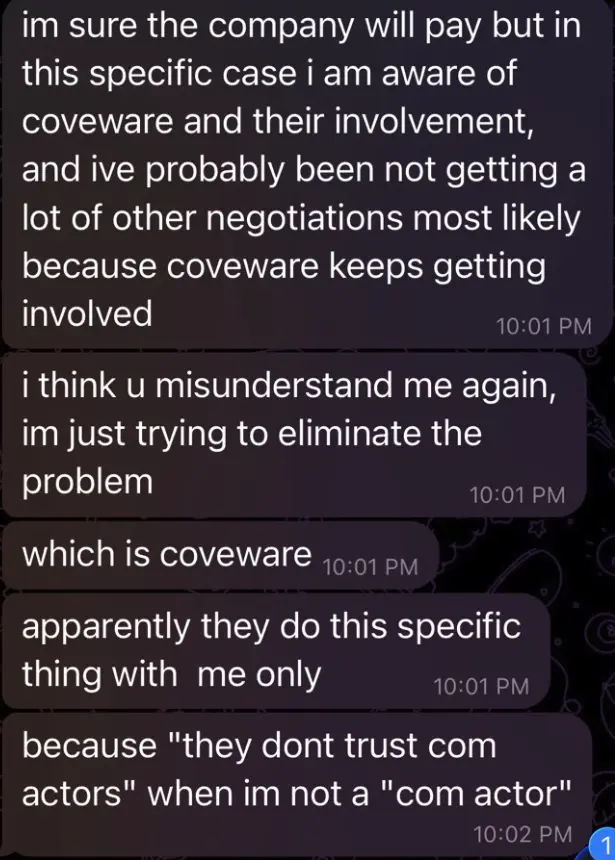
Internal communications recovered by investigators demonstrate the extent to which this principled security advice disrupted the hackers’ business model. In private Telegram chats from April and May 2026, the primary administrator of the ShinyHunters account complained bitterly to co-conspirators about Coveware, lamenting that the firm’s anti-ransom advisories were severely damaging their collection rates and actively preventing victims from paying. In one chat, the administrator noted an intent to "eliminate the problem." Coveware declined to comment on the disclosures.
Industry leaders argue that the compensation structures common among negotiation firms create inherent conflicts of interest. Mark Camillo, chief executive of CyberAcuView—an industry group established by major cyber insurance carriers—noted that while some firms charge flat retainers, others take a percentage of the total ransom paid. Camillo pointed out that this percentage-based model provides negotiators with a clear financial incentive to encourage payouts and discourage aggressive reductions in ransom amounts, introducing misaligned incentives into an already critical ecosystem.
Federal prosecutors have increasingly targeted these corrupt relationships. On October 7, the Department of Justice charged MonsterCloud CEO Zohar Pinhasi with wire fraud and conspiracy, alleging he charged clients millions for remediation while secretly paying hackers behind his customers’ backs. Earlier in the year, Florida-based ransomware negotiator Angelo Martino was sentenced to 70 months in prison for conspiring with the BlackCat/ALPHV ransomware group to extort victims by leaking confidential client negotiating positions to maximize payouts.
 Pevita Pearce
 Dwi Wanna