
 By Dwi Wanna
Federal Bureau of Investigation agents in Pennsylvania have arrested a prominent Canadian cybersecurity executive on federal charges connecting him to the notorious ShinyHunters hacking collective. The arrest comes amid an escalating, high-stakes federal investigation into the cybercrime group, which recently executed a brazen breach that compromised sensitive personnel records of thousands of law enforcement agents.
According to multiple sources familiar with the ongoing probe, the suspect was taken into custody earlier this week while visiting Pennsylvania to attend a major industry gathering. The New York Times first reported the arrest of the Canadian national on suspicion of providing assistance to the ShinyHunters syndicate, though neither initial news reports nor a brief public statement posted to social media by FBI Director Kash Patel explicitly named the individual at the time of the announcement.
Sources close to the investigation indicate that the arrested executive was in the state to participate in the Cyber Risk Summit, a prominent annual conference held between October 5 and October 7 at the Loews Philadelphia Hotel. The suspect’s professional background centers heavily on specialized advisory services, ransomware negotiations, and crisis management for corporate entities facing cyber extortion. Publicly available event materials and online records show that the summit featured numerous prominent sponsors, with the largest sponsorship backing provided by Cypfer, a well-known Canadian cybersecurity and incident response firm.
Professional networking profiles on LinkedIn indicate that Edward Dubrovsky, a veteran figure in the Canadian cybersecurity sector, has previously been associated with Cypfer, where his online history identified him as an ex-founder and managing director. Dubrovsky’s professional footprint later extended to CyberSteward, another Canadian security firm and conference sponsor. Approximately one month prior to his arrest, Dubrovsky shared posts on social media indicating his intention to travel to Philadelphia to attend the Cyber Risk Summit alongside his colleagues from the CyberSteward team.

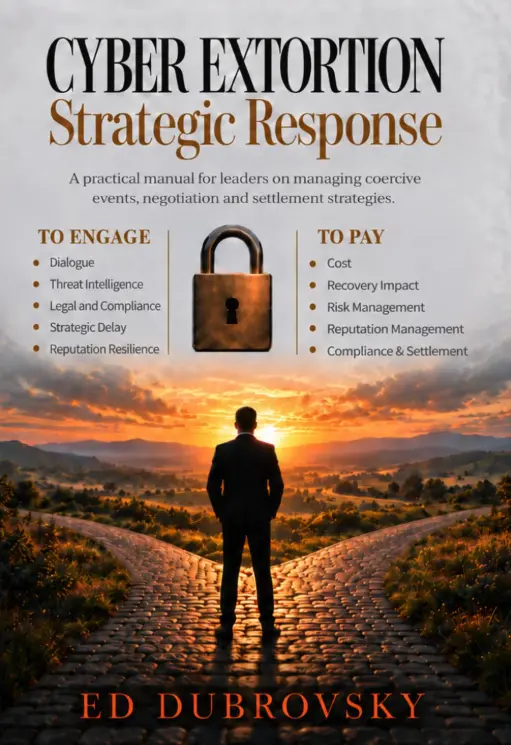
In the wake of the arrest, representatives for Cypfer clarified that Dubrovsky’s title as a founder or co-founder on his public profile was inaccurate, noting instead that he had served in the capacity of a managing director prior to his resignation from the firm in December 2025. In previous professional commentary and online publications, Dubrovsky frequently emphasized the intricate nuances of handling coercive digital threats. His professional writing and public statements routinely highlighted strategies for navigating high-stakes corporate extortions while remaining aligned with global compliance standards. He is also the author of a 252-page industry publication titled Cyber Extortion Strategic Response, a manual designed to guide organizations through the complex decision-making processes required during ransomware events. Excerpts from the book’s publishing listings emphasize a core philosophy that communicating with cybercriminals is distinct from negotiating a payout, and that engagement can serve tactical objectives such as testing attacker claims, gathering intelligence, and buying time.
Federal court documentation filed in Pennsylvania reveals that an individual matching the suspect’s identity—under the slightly misspelled name Edward Dobrovsky—was formally charged with federal cyber extortion and conspiracy offenses on October 8. While several critical case files, including the foundational criminal complaint, remain sealed from public view, a subset of documents indexed on legal research platforms outline the primary accusations. The charges formally accuse the defendant of engaging in a conspiracy to threaten the impairment of information confidentiality with the intent to extort money, alongside charges of interfering with commerce through threats.
Inmate records maintained by the U.S. Bureau of Prisons reflect that a 54-year-old individual named Edward Dubrovsky was initially detained at a federal detention facility in Philadelphia following the operation. However, court dockets include administrative notices filed on October 9 directing the transfer of the legal proceedings to the U.S. District Court for the Eastern District of Texas. Legal sources indicate that this district has become the central operational hub and geographic epicenter for the multifaceted federal investigation into the ShinyHunters organization. Representatives for the FBI declined to offer public comments regarding the specifics of the ongoing judicial proceedings.
Available court documents indicate that the defendant has not yet retained private legal counsel, nor has the court formally appointed a public defender to represent him in the matter.
The ShinyHunters collective has long posed a severe challenge to international cybersecurity enforcement, typically utilizing sophisticated phishing campaigns and stolen credential sets to infiltrate corporate software-as-a-service accounts. Once inside corporate networks, the group siphons vast quantities of proprietary and confidential data, subsequently threatening to leak the stolen material publicly unless substantial cryptocurrency ransom demands are satisfied. According to assessments shared by federal law enforcement officials, the cybercrime syndicate has successfully extorted more than $70 million from corporate and institutional victims over the course of the year.

The apprehension of the Canadian cybersecurity executive represents the latest milestone in a rapidly unfolding international crackdown on the hacking network. Investigators have spent recent weeks combing through digital evidence and hardware devices seized by law enforcement authorities in Europe. Last month, Dutch police executed an operation resulting in the arrest of Pepijn van der Stap, a reformed cybercriminal linked by investigators to the ongoing ShinyHunters inquiry. Sources indicate that federal prosecutors are actively weighing additional criminal charges against principals and associates at other firms operating within the specialized niche of ransomware negotiation and incident response.
The pressure on federal investigators intensified dramatically immediately following the arrest of Van der Stap. In the wake of that law enforcement action, another prominent figure within the ShinyHunters leadership hierarchy, operating under the alias "Rey," assumed operational control of the collective. This individual began actively taunting federal authorities, specifically boasting about a high-profile cyber intrusion that compromised an online recruitment portal maintained by the FBI itself. That breach exposed sensitive personal data belonging to bureau personnel, including unit assignments, professional specializations, and confidential medical and psychiatric records.
Investigative reporting later revealed that the individual operating as "Rey" was a teenager named Saif Al-din Khader. Authorities successfully located and detained Khader, who has since begun cooperating with federal investigators. Court and investigative disclosures revealed that Khader’s apprehension occurred just as the collective was attempting to execute a coercive extortion campaign against a digital navigation and aviation unit that had been divested by aerospace giant Boeing in late 2025.
 Laily UPN
 Pevita Pearce