
 By Lina Hope
Federal Bureau of Investigation agents have arrested a high-ranking executive from a Canadian cybersecurity firm in Pennsylvania, marking a significant escalation in the ongoing, high-stakes international investigation into the notorious "ShinyHunters" cybercrime syndicate. The arrest comes on the heels of a brazen cyberattack attributed to the group that compromised sensitive internal records belonging to the bureau itself, exposing confidential data concerning thousands of law enforcement agents.
Multiple sources familiar with the matter confirmed the arrest to KrebsOnSecurity, noting that the federal sweep targets the intersection of corporate cybersecurity advisory services and high-level digital extortion. The high-profile arrest was first reported by The New York Times, which detailed that a Canadian man had been taken into custody in Pennsylvania on suspicion of providing material assistance to the ShinyHunters operation. While neither the initial newspaper report nor a brief public statement posted to social media by FBI Director Kash Patel explicitly named the individual in custody, federal court records and industry sources have since illuminated the identity of the suspect and the broader scope of the federal inquiry.
According to sources close to the investigation, the Canadian national traveled to Pennsylvania to attend a prominent cybersecurity and insurance conference. The suspect’s professional background is deeply rooted in the niche sector of handling complex ransomware negotiations and advising corporate victims on how to manage extortion demands from cybercriminal organizations. Control over the multi-jurisdictional ShinyHunters investigation has recently been centralized at a primary FBI field office in Texas, signaling the growing gravity of the federal probe as investigators untangle the network of facilitators supporting the group.
Publicly available event registries indicate that the annual Cyber Risk Summit was hosted at the Loews Philadelphia Hotel. The conference featured various industry sponsors, with financial and logistical backing from several prominent security vendors. Among them was a major Canadian cybersecurity firm known as Cypfer. According to public professional networking profiles, an individual identified as Edward Dubrovsky previously held a leadership role at Cypfer before transitioning to another Canadian security firm and conference sponsor, CyberSteward. Approximately one month prior to his arrest, Dubrovsky shared details on professional platforms regarding his plans to attend the Philadelphia summit alongside his new corporate team.

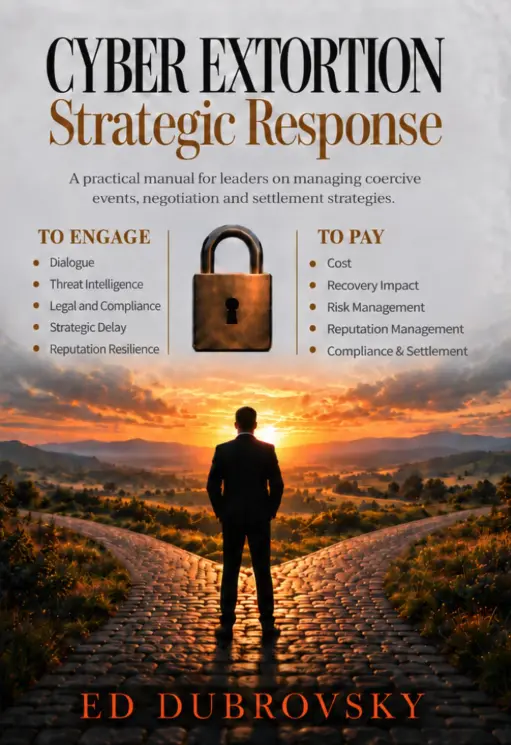
A spokesperson for Cypfer subsequently clarified Dubrovsky’s former association with the company, noting that he served as a managing director prior to his resignation in December rather than holding a founder or co-founder status as indicated on his public profile. Dubrovsky’s professional footprint in the industry also includes authorship of a 252-page textbook focused on the strategic response to digital extortion and the intricate dynamics of managing ransomware negotiations. Promoted as a guide to help organizations navigate the critical decisions required during cyber incidents, the book emphasizes a core philosophy distinguishing dialogue from payment: communicating with a digital extortionist does not equate to agreeing to financial terms, and engagement can serve alternative objectives such as information gathering and buying time.
Federal court documents filed in Pennsylvania reveal that an individual named Edward Dobrovsky—reflecting a slight spelling variation in the court filings—was taken into custody on charges connected to cyber extortion and conspiracy. While several key documents, including the primary criminal complaint, remain sealed from public view, a subset of the docket has been indexed on legal transparency platforms. These records outline preliminary charges accusing the defendant of conspiracy to threaten the impairment of information confidentiality with the intent to extort money, alongside charges of interference with commerce through threats.
U.S. Bureau of Prisons records initially indicated that a 54-year-old individual matching the suspect’s description was being housed at a federal detention facility in Philadelphia. However, subsequent court notices filed in the docket directed the immediate transfer of the legal proceedings to the U.S. District Court for the Eastern District of Texas, aligning with information from sources indicating that the Texas field office has become the operational epicenter for the comprehensive federal investigation into the ShinyHunters collective. Representatives for the FBI declined to comment on the specifics of the ongoing judicial proceedings.
Available court documentation indicates that the defendant has not yet retained private legal counsel, nor has a public defender been formally appointed by the court. Representatives for CyberSteward have not immediately responded to requests for comment regarding the arrest of their associated executive.
The ShinyHunters hacking syndicate has long established a formidable reputation within the global cybercrime ecosystem by utilizing targeted phishing campaigns and stolen corporate credentials to siphon proprietary data from Software-as-a-Service providers and enterprise cloud environments. Once inside corporate networks, the group typically pressures victims by threatening to leak sensitive data publicly unless substantial cryptocurrency ransoms are fulfilled. According to estimates provided by federal law enforcement agencies, the collective has successfully extorted upwards of $70 million from corporate and institutional victims over the course of the year.

The latest enforcement action follows a series of coordinated international operations aimed at dismantling the infrastructure supporting the hacking group. Investigators have spent weeks analyzing electronic devices seized during a late-September raid executed by Dutch law enforcement authorities, which resulted in the arrest of reformed cybercriminal Pepijn van der Stap in connection with the broader ShinyHunters inquiry. Industry insiders suggest that additional criminal charges against principals and associates at other firms specializing in ransomware mediation and cyber incident response may be forthcoming as prosecutors continue to map out the network’s financial and logistical conduits.
The pressure surrounding the investigation intensified dramatically immediately following Van der Stap’s apprehension. A prominent figure within the hacking collective operating under the online pseudonym "Rey" assumed leadership of the group and initiated a brazen campaign taunting federal authorities. This digital taunting included public challenges regarding the theft of sensitive data extracted from an online recruitment portal utilized by the FBI itself. The compromised material reportedly included granular personnel records detailing individual unit assignments, professional specializations, and confidential medical and psychiatric histories of bureau personnel.
International media reports subsequently identified "Rey" as a teenager named Saif Al-din Khader. Authorities detained the young hacker, who has since begun cooperating with federal investigators. Law enforcement tracks converged on the suspect as the cybercrime unit allegedly attempted to execute an extortion campaign against a digital aviation and navigation unit that had been divested by aerospace giant Boeing. As federal prosecutors and field agents continue to untangle the web of complicity surrounding the syndicate’s multi-million-dollar extortion operations, the investigation remains an active and fast-moving federal priority.
 Pevita Pearce
 Dwi Wanna