
 By Siti Muinah
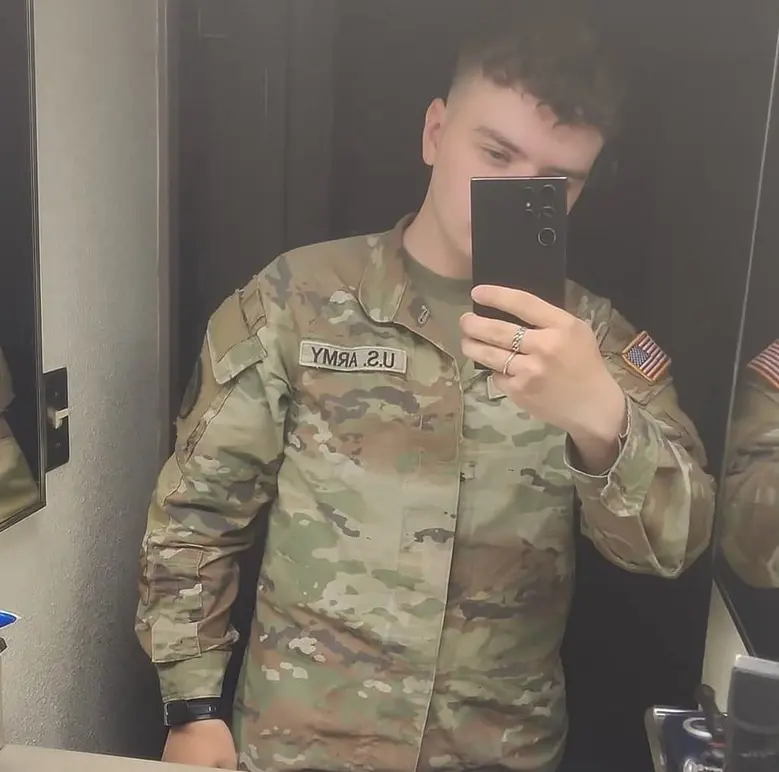
A former U.S. Army soldier who admitted to hacking into multiple telecommunications companies and stealing mobile call and text metadata belonging to more than 100 million AT&T customers was sentenced to 70 months in federal prison. In addition to the nearly six-year prison term handed down by a federal judge in Seattle, the defendant was ordered to pay approximately $294,978 in restitution to his victims, bringing a significant chapter of a sprawling, international cybercrime investigation to a close.
Cameron John Wagenius, 22, was stationed at a U.S. Army base in South Korea when he operated under the online cybercriminal moniker “Kiberphant0m.” Collaborating with a network of alleged co-conspirators, Wagenius exploited compromised credentials left unprotected by organizations utilizing the cloud data storage service Snowflake. Because these specific accounts failed to enforce multi-factor authentication (MFA)—a security oversight that Snowflake has since addressed by mandating MFA across all platforms—the hackers were able to infiltrate vast repositories of sensitive corporate data.
The scope of the operation became public knowledge in October 2024, when Wagenius took to cybercrime forums to boast about his illicit achievements. He claimed to have successfully exfiltrated the call and text metadata—including crucial details such as source and destination phone numbers, timestamps, and call durations—for tens of millions of AT&T customers. Furthermore, Kiberphant0m asserted that he had breached more than a dozen telecommunications companies worldwide, including Verizon’s specialized Push-to-Talk business, and subsequently engaged in public extortion schemes, threatening to publish the stolen proprietary and customer data unless his demands were met.
The trail leading to his identification began to take shape in late November 2024, when security journalism outlet KrebsOnSecurity published findings indicating that the individual operating as Kiberphant0m was likely an active-duty U.S. soldier stationed in South Korea. The reporting accelerated law enforcement action; less than a month later, Wagenius was apprehended, subsequently facing two separate federal indictments. Confronted with the evidence assembled by federal investigators, he swiftly pleaded guilty to all counts across both cases.
While Wagenius served as a central figure in the attacks, federal prosecutors revealed that his extortion efforts were supported by Kenneth Schuchman, a 28-year-old resident of Vancouver, Washington, who possesses an extensive background in cybercrime. Schuchman’s criminal history includes a high-profile 2019 guilty plea for operating the Satori botnet, a massive, weaponized network of compromised Internet-of-Things devices utilized to orchestrate devastating, large-scale distributed denial-of-service attacks.
Wagenius was not alone in facing scrutiny over the Snowflake-related data thefts. Two other alleged co-conspirators have been targeted by the justice system. Conor Riley Moucka, operating under the alias “Judische” and based in Kitchener, Ontario, was arrested in 2024 and entered a guilty plea in August 2026. Another co-conspirator, John Erin Binns, an American citizen currently residing in Turkey, remains wanted by authorities. Binns is also sought in connection to a massive 2021 data breach at T-Mobile that exposed the personal identifying information of at least 76 million customers.
The extortion ring’s tactics extended beyond initial corporate blackmail into the realm of re-extortion and threats involving national security assets. Following Moucka’s arrest—and even after AT&T had already transferred a $370,000 Bitcoin ransom to the extortion group—Kiberphant0m escalated his campaign. He published materials on hacker forums that he claimed included AT&T call logs belonging to then-President-elect Donald Trump and then-Vice President Kamala Harris, alongside technical schematics allegedly stolen from the U.S. National Security Agency.
The unique and alarming nature of the case triggered a joint multi-agency federal response. Paul Russell, a resident agent in charge at the Defense Criminal Investigative Service—the criminal investigative arm of the U.S. Department of Defense Office of Inspector General—explained that the investigation ramped up immediately upon discovering that an active-duty soldier with a secret security clearance was allegedly developing hacking tools and trafficking in stolen data. Russell noted that encountering an insider threat of this caliber is exceptionally rare, prompting immediate, intensive collaboration between DCIS, the Federal Bureau of Investigation, the Army Criminal Investigative Division, and the U.S. Secret Service due to the unknown magnitude of the security risks involved.
Despite the gravity of his offenses and the massive volume of data compromised, a sentencing memorandum filed by federal prosecutors in Seattle revealed a striking detail: Wagenius’s elaborate criminal enterprise yielded remarkably little financial return. Investigators calculated that, despite stealing data of immense theoretical value from major telecommunications providers, Wagenius earned a total of only about $1,500 from his sales of stolen information. The government’s sentencing memo underscored this disparity, stating that while Wagenius achieved minimal financial success as a cybercriminal, his actions deliberately caused profound harm to individual citizens, major U.S. corporations, and the federal government.
Compounding his legal troubles, Wagenius continued his illicit technical explorations even while incarcerated and awaiting sentencing. According to the government’s sentencing memo, prison records from September 2025 demonstrated that Wagenius violated Bureau of Prisons computer use policies. Utilizing another inmate’s email system, he attempted to gather information on software vulnerabilities by instructing the email recipient to prompt commercial artificial intelligence tools. His queries specifically sought Windows 10 Enterprise privilege escalation paths, specific Common Vulnerabilities and Exposures (CVEs) complete with working exploits, and step-by-step instructions for exploiting older D-Link networking hardware known as CVE-2023-45208.
Furthermore, records indicated that Wagenius used similar proxy methods to research methods for constructing improvised antennas using prison commissary items to extend radio reception, as well as inquiring about prison escape strategies. When confronted by authorities about these activities, Wagenius attempted to frame his AI queries as research for a book he claimed to be writing—a technique mirroring prompt injection, where attackers bypass AI safety guardrails by embedding malicious technical requests within creative or hypothetical writing prompts. While prosecutors noted they found no evidence that Wagenius successfully deployed these vulnerabilities within the prison’s computer systems, the conduct highlighted an ongoing technical fixation that factored into the final judicial proceedings.
 Pevita Pearce
 Dwi Wanna