
 By Asro
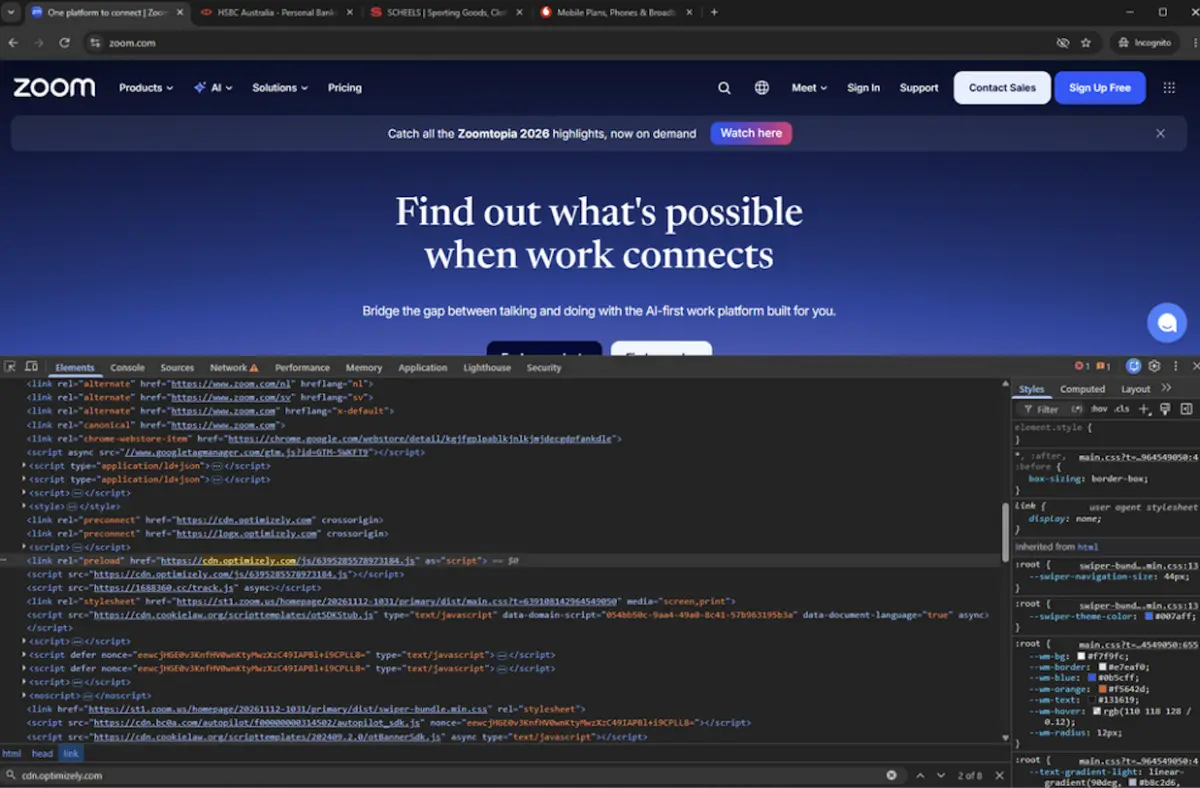
At least 178 top-tier web destinations unwittingly served a variety of sophisticated malware exploits against unsuspecting visitors over a recent 24-hour period, a security incident triggered by a vulnerability involving Optimizely, a prominent industry platform that helps websites customize user experiences and conduct digital feature testing. Cybersecurity experts say the incident, which saw data-stealing malicious software silently injected into high-profile sites including the BBC, CNN, Equifax, Ledger, and Zoom, was severely exacerbated by the reality that very few popular websites enforce strict rules or governance on the origins of third-party content.
According to an incident analysis published by the security firm Report URI, malicious JavaScript code was served to visitors across 178 organizations through Optimizely’s platform. Report URI researcher Scott Helme wrote that the malicious payload delivered via the tampered JavaScript was continuously rebuilt and modified 26 times throughout the day. This dynamic approach dropped a multi-purpose malware kit designed to siphon payment card data, harvest sensitive browser cookies, capture screenshots, and silently swap any cryptocurrency payment addresses displayed on the page with those controlled by the attacker.
Helme noted that the affected websites also served exploit code specifically tailored to target known vulnerabilities residing within older Apple iPhone and iPad operating systems. Known widely in the threat intelligence community by monikers such as "DarkSword" and "Coruna," these represent zero-click exploit kits capable of chaining together a half-dozen underlying security flaws to seize complete control over outdated mobile devices and aggressively extract stored personal data.
The incident underscores a systemic blind spot in modern web architecture. As Helme emphasized in his published findings, trusted JavaScript does not always remain trustworthy. A mainstream website can be thoroughly compromised through a third-party dependency without its own internal code infrastructure ever being breached directly by an adversary.
When contacted for comment regarding the security breakdown, Optimizely stated that it identified a security incident in which an unauthorized party successfully exploited a vulnerability within the Optimizely Experimentation framework to inject malicious JavaScript code into select customer projects.
In a formal written statement shared by the company, representatives noted that they acted swiftly to contain the developing situation and have fully remediated the identified vulnerability. These defensive measures included blocking access to the vulnerable path, deploying an immediate code fix, removing all injected malicious code from affected projects, terminating active user sessions, revoking security tokens, and resetting access permissions for all impacted user accounts. Furthermore, Optimizely stated that it implemented additional protections to prevent malicious code from being delivered through Cloudflare, and while the immediate incident has been fully addressed, the company continues working alongside third-party cybersecurity experts to conduct a comprehensive internal investigation.
The vulnerability highlights the delicate balancing act inherent in modern web development, where many leading properties refuse to fully render or display content unless visitors consent to let dozens of third-party vendors execute JavaScript. As a powerful web scripting language that enables interactive elements, animations, and dynamic features, JavaScript executes directly on the user’s local device. This grants the code considerable power to read information displayed within the browser environment, track user interactions, and even modify a website’s visual appearance or underlying content structure.
The heavy reliance on JavaScript is driven largely by the need for precise browser fingerprinting, robust analytics, and audience tracking. According to the 2025 Web Almanac compiled by the HTTP Archive, the median homepage loads a minimum of 22 distinct JavaScript files. However, as the recent Optimizely compromise vividly demonstrates, a security lapse at a third-party vendor can instantly snowball into a sprawling supply chain attack, forcing downstream websites to serve tampered, malicious files directly to their trusting user base.

Zach Edwards, a researcher at Infoblox and co-founder of the ad-tracking service DecryptAds, explained that Optimizely operates as a vendor that frequently collects data outside standard user consent flows. Because its primary function is A/B testing and user experience optimization, Optimizely’s JavaScript snippets are typically embedded as close to the very top of a webpage’s HTML structure as possible to ensure it is among the earliest elements to render upon loading.
To make the product function smoothly as expected, this code is engineered to fire immediately upon page load without restricting its execution behind a user consent dialog box, Edwards pointed out. Consequently, this particular supply chain attack required no active clicking, interaction, or consent from the visitor to trigger; most of the impacted client websites automatically served the malicious payload the exact moment a user loaded the page, dramatically amplifying the risks associated with compromised third-party marketing and testing snippets.
Industry experts emphasize that website operators can significantly minimize the probability that a breach at a content provider spirals into a full-scale supply chain attack by fully utilizing Content Security Policies, commonly referred to as CSPs. These security headers explicitly define the authorized domain names permitted to serve third-party content and scripts to a website’s visitors. Yet, as Edwards pointed out, the vast majority of websites—with the notable exception of the largest e-commerce operations, social media networks, and financial institutions—either fail to implement CSPs entirely or maintain policies that are far too permissive to satisfy marketing and advertising requirements.
Across the Web, if a platform embeds third-party JavaScript resources without a robust Content Security Policy in place, any compromised partner can effortlessly inject new, unauthorized domains into the host website without facing any technical barriers, Edwards noted. The digital ecosystem has firmly entered the age of JavaScript supply chain attacks, yet organizations rarely discuss the foundational purpose of Content Security Policies as a viable remedy for operators, even if initial deployment can occasionally present technical friction.
A review of the websites impacted by the Optimizely incident reveals a stark lack of effective defensive architecture. According to data compiled by Report URI, 68 of the affected sites had no Content Security Policy configured at all, while another 50 sites maintained a CSP that was permissive enough to allow both the malware payload to execute and the subsequent data theft to succeed. Only 24 of the affected sites, representing roughly 15 percent of the total, possessed CSP configurations that successfully blocked the malicious payload from executing.
Broadening the scope to the wider internet, the overall deployment of CSPs across the web’s busiest destinations remains low at approximately 10 percent, according to statistics from Helme’s scanning project crawler.ninja, which evaluates the top one million websites daily for security vulnerabilities. Helme expressed hope that the high-profile nature of this incident will inspire a broader wave of adoption for effective CSPs, noting that the outcome could have been far worse. Based on Report URI’s preliminary estimates, the threat actors behind the campaign managed to siphon approximately $7,500 worth of virtual currency from affected users, alongside an undetermined volume of stolen payment card records.
Reflecting on the systemic vulnerability of the modern web, Helme likened the prevailing lack of defensive controls to the Wild West. Organizations continue running vast amounts of third-party code without possessing clear visibility into its actual execution behavior, making large-scale security breaches inevitable in environments lacking basic checks and rules. Once an attacker successfully gains the capability to execute arbitrary code on a major web property, the primary limiting factor becomes their intent and their ability to script the desired outcome—a hurdle that automated tools and artificial intelligence have largely eliminated.
For individual internet users seeking absolute control over the scripts executing within their browsers, traditional script-blocking extensions like NoScript offer a reliable defense. However, such tools have historically appealed primarily to privacy-conscious enthusiasts and security professionals willing to manually review and approve dozens of individual JavaScript requests on every newly visited website.
In contrast, modern ad-blocking software has evolved to capably intercept and neutralize the vast majority of potentially risky third-party JavaScript requests automatically. While standard cybersecurity guidance a decade ago prioritized foundational antivirus software and local firewalls, contemporary threat landscapes suggest that a robust ad and script blocker frequently serves as an essential digital firewall for everyday web navigation.
 Ammar Sabilarrohman
 Laily UPN
 Muslim