
 By Ali Ikhwan
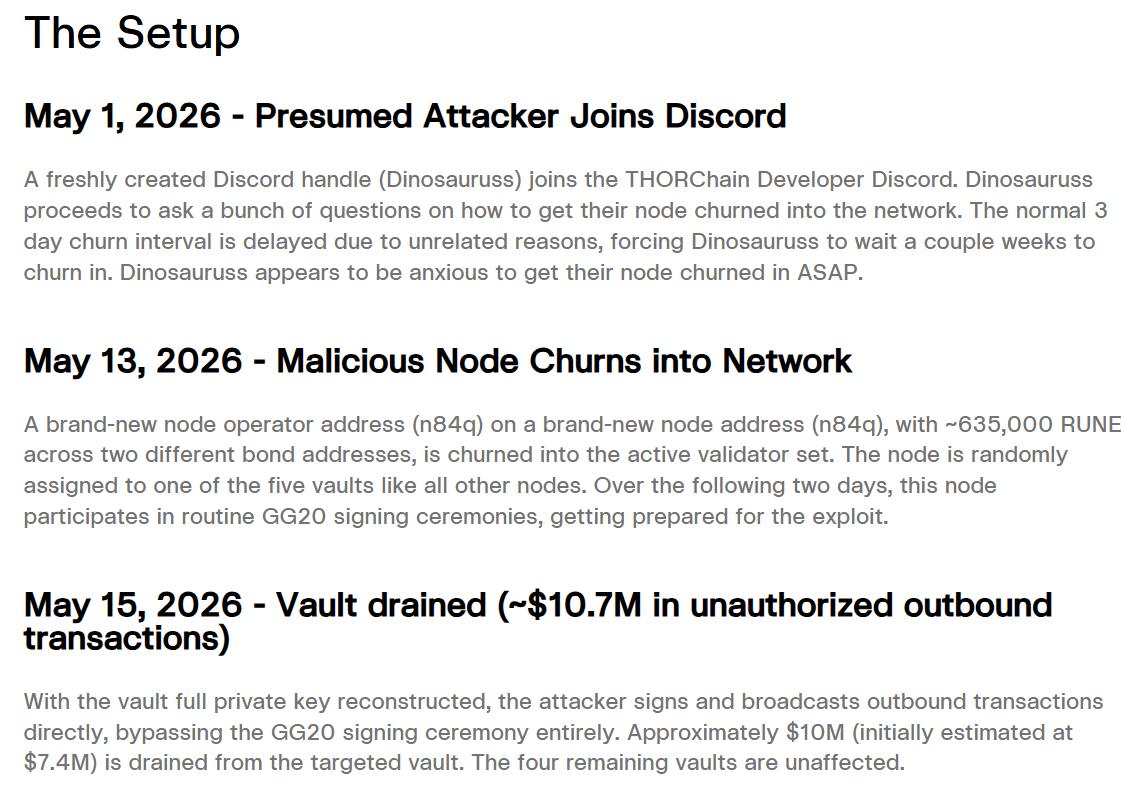
Decentralized liquidity protocol THORChain is navigating the aftermath of a major security breach that resulted in the loss of approximately $10.7 million from one of its core vaults. According to post-mortem details released by the protocol, the exploit was executed by a malicious node operator who successfully capitalized on a critical vulnerability within the system’s threshold signature scheme.
The incident, which was initially brought to light by blockchain investigator ZachXBT a week prior to the official disclosure, underscores the ongoing vulnerability risks facing cross-chain liquidity networks. The breach occurred within THORChain’s GG20 threshold signature scheme (TSS), a cryptographic architecture designed to secure user vaults by decentralizing key control across multiple independent node operators. Under normal operating conditions, this setup ensures that no single node ever holds the full private key, thereby eliminating a single point of failure.
However, the recent incident demonstrated how sophisticated actors could manipulate this mechanism. The protocol revealed that the vulnerability allowed the malicious node operator to reconstruct a complete private key for a single vault through a process known as "progressive key material leakage." By systematically gathering fragmented data over time, the attacker managed to bypass the distributed safety guarantees of the GG20 framework and siphon off millions in digital assets.
Despite the severity of the breach, THORChain’s automated defensive mechanisms played a crucial role in mitigating broader damage. The protocol’s automatic solvency checks triggered within minutes of the anomalous activity, swiftly halting both signing and trading operations across multiple supported blockchain networks without requiring human intervention. Following this automated response, node operators quickly coordinated via Discord to execute a full network halt within two hours of the initial detection. They subsequently deployed an emergency patch to address the underlying vulnerability.
The post-mortem report confirmed that these automated safeguards functioned as intended, effectively preventing the exploiter from draining additional funds from other vaults. The timing of the incident coincides with a broader resurgence in cryptocurrency exploits across the decentralized finance ecosystem, with DefiLlama data indicating that more than $634 million was stolen through various hacks and exploits during the month of April alone.
THORChain Weighs Recovery Path Without RUNE Sales
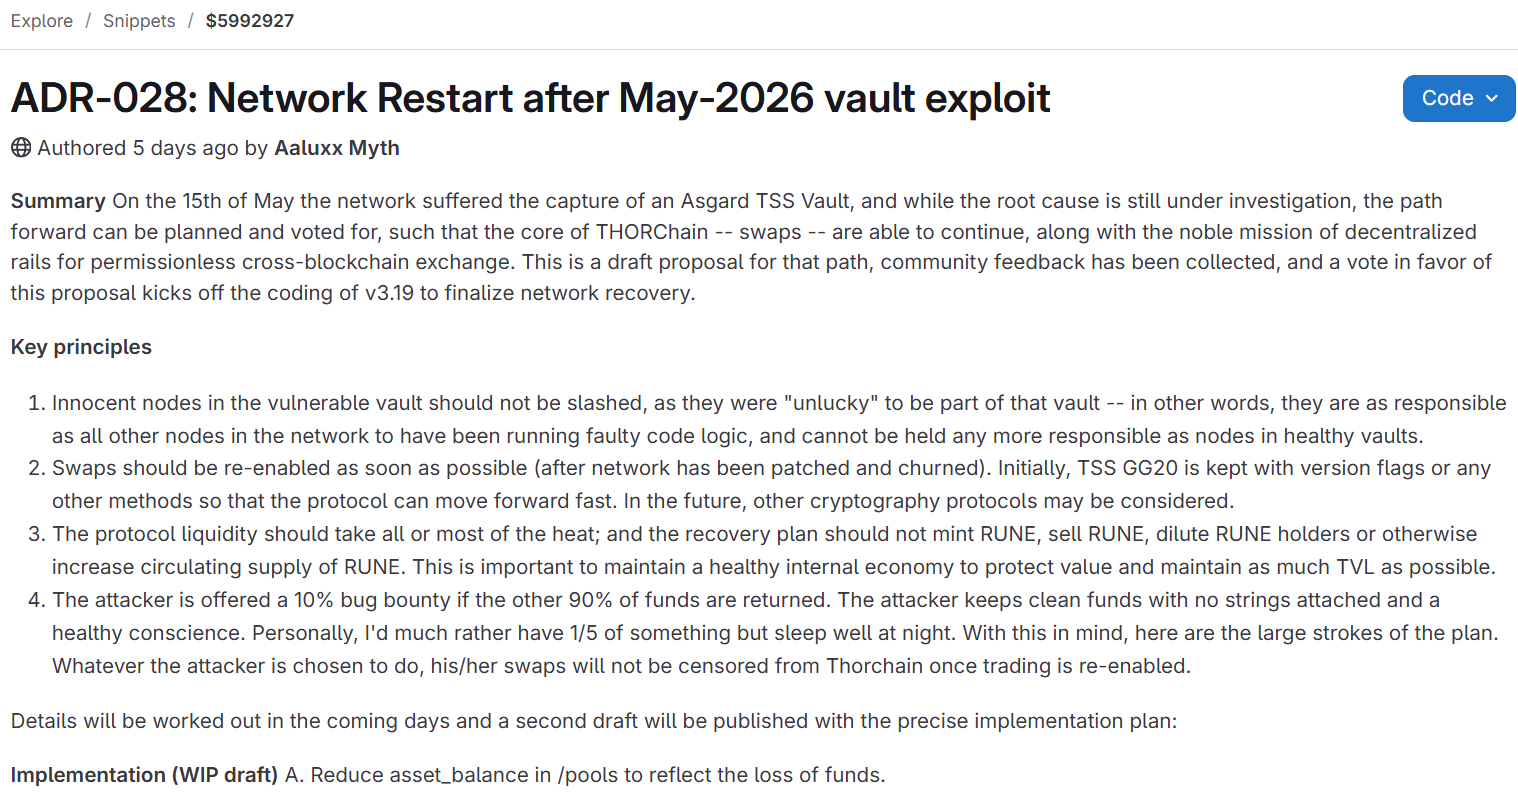
As the network works to stabilize following the security breach, THORChain leadership and community members have turned their focus toward formulating a comprehensive recovery plan. On Friday, the protocol outlined its proposed post-exploit recovery path through governance proposal ADR-028, which was published on GitLab and opened for official voting among node operators.
The proposed governance measure establishes a structured approach to covering the $10.7 million deficit without resorting to the minting or sale of THORChain’s native RUNE tokens. Under the terms of ADR-028, the protocol would first absorb the financial losses using existing protocol-owned liquidity. Any remaining balance would then be distributed proportionately across synth holders. While this strategy would temporarily deplete the protocol’s owned liquidity reserves, it includes a mechanism to redirect a designated portion of future protocol income to systematically replenish those funds over time.
In tandem with the governance proposal, THORChain introduced a recovery bounty aimed at incentivizing the return of the stolen funds. The protocol also confirmed plans to heavily slash the stake of the malicious node operator responsible for the exploit, while implementing measures to protect innocent nodes that happened to be assigned to the same compromised vault.
ADR-028 explicitly recommends maintaining the existing GG20 TSS framework, albeit in a patched and upgraded iteration, and mandates that cross-chain trading will remain suspended until the software updates are thoroughly tested and verified. Addressing the decision to stick with the current cryptographic standard rather than migrating immediately to an alternative, THORChain co-founder Chad Barraford explained that adopting a new standard carries its own set of unproven risks.
"We are staying with GG20 for now, because if we move to another standard, it could have vulnerabilities too," Barraford told Cointelegraph. He noted that while transitioning to an alternative standard such as DKLS had already been outlined on the protocol’s development roadmap for the year, other priorities had previously delayed its implementation. "Moving to DKLS was on our roadmap for this year. It was pushed out due to other priorities. But obviously now we are taking a closer look at it (and others)," Barraford added.
The decision to retain an upgraded version of the GG20 framework has elicited a mixed reception from developers, analysts, and investors within the wider cryptocurrency community. Pseudonymous crypto project analyst Bird evaluated the initial vulnerability, suggesting that the root cause pointed toward a potential "flaw in randomness generation or local signing isolation" within the GG20 TSS signing stack. At the same time, Bird commended THORChain’s automated safeguards for successfully limiting the overall extent of the financial damage.
Other industry observers adopted a more skeptical stance regarding the long-term viability of the cryptographic scheme. Expressing concern over the underlying architecture, crypto investor JP shared a critical perspective in a post on X, writing, "My mental model is that GG20 has many brittle assumptions. You can keep patching it, but it will forever be a bit of a black box."
Market response to the security incident was reflected in the valuation of the protocol’s native asset. CoinMarketCap data indicates that the price of the RUNE token declined by approximately 15.5% over the course of the week following the initial exploit disclosure. However, the token subsequently demonstrated signs of resilience, staging a modest 4% recovery in the 24-hour period leading up to Friday morning, as community members weighed the governance proposals and monitored the network’s path toward resuming normal operations.
 Neng Nana
 Suro Senen
 Siti Muinah