
 By Evan Lee Salim
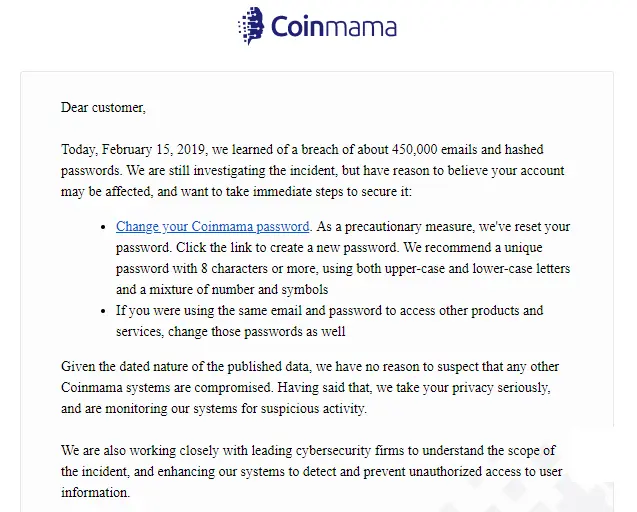
One of the most prominent cryptocurrency brokerage platforms in the global digital asset ecosystem has fallen victim to a severe security incident. Coinmama, a well-known service enabling users to purchase cryptocurrencies easily, experienced a data breach on February 15. The malicious intrusion resulted in the compromise of sensitive user information, specifically email addresses and hashed passwords, affecting over 450,000 registered accounts.
The security event was part of a larger, coordinated data leak involving approximately 24 different websites and applications associated with Coinmama, exposing a staggering total of roughly 747 million data records across the broader digital landscape. Despite the massive volume of compromised records tied to the infrastructure, Coinmama’s overall user base remains substantial, boasting more than 1.3 million registered individuals worldwide.
The Discovery and Immediate Response
Moments after the unauthorized access was detected, the platform’s management and internal cybersecurity teams took swift, decisive measures to contain the breach. The intervention came immediately after security analysts discovered that a compiled list of the compromised user credentials had been leaked and was circulating on the dark web.
According to comprehensive internal investigations conducted by Coinmama’s security team, the scope of the incident was successfully limited, with approximately 450,000 active users ultimately impacted. Further analysis revealed that the affected individuals were predominantly legacy users who had created their accounts on the brokerage platform prior to August 5, 2017.

Crucially, despite the exposure of email addresses and login credentials, the platform confirmed that no cryptocurrencies were stolen during the cyberattack. Furthermore, investigations indicated that none of the leaked login information had been successfully exploited by malicious actors to gain unauthorized access to user trading accounts or wallets.
In response to the discovery, Coinmama swiftly mobilized to notify all affected customers, urgently advising them to update their login credentials and secure their accounts to prevent any potential downstream exploitation of the leaked data. Additionally, executive management pledged to undertake a comprehensive overhaul and strengthening of the platform’s underlying security architecture, aiming to fortify defenses and prevent similar unauthorized access incidents in the future.
A Wider Trend of Database Vulnerabilities
Coinmama is far from the only prominent online platform to experience this type of malicious intrusion in recent years. Other widely used consumer services, such as the fitness tracking application MyFitnessPal and the dating platform Coffee Meets Bagel, have previously fallen victim to similar large-scale data breaches.
According to security experts, these incidents often share common technological denominators. Speaking to technology publications, Ariel Ainhoren, a threat intelligence researcher from IntSights, shed light on the mechanics behind these attacks. Ainhoren explained that a specific database software vulnerability—most notably involving PostgreSQL database implementations—had been repeatedly exploited by threat actors to compromise multiple large databases across various independent web platforms. Once malicious actors successfully penetrated the main system architecture, this particular vulnerability allowed them to efficiently exfiltrate and download extensive database records across multiple associated websites simultaneously.

Tricky Timing for the Cryptocurrency Market
The timing of the security breach at Coinmama could hardly have been worse for the broader digital asset industry. The incident unfolded just as damaging reports were widely circulating concerning another major crypto entity, the Canadian exchange QuadrigaCX, which had lost control of millions of dollars in customer funds stored across inaccessible cold wallets following the sudden death of its founder.
Incidents of this magnitude inevitably deal a blow to public perception, causing widespread anxiety and eroding user confidence in cryptocurrency markets and centralized digital asset exchanges in particular. This is precisely the kind of negative publicity that mainstream platforms strive to avoid, as building long-term trust remains a primary hurdle for the broader adoption of decentralized finance and digital currencies.
Furthermore, the Coinmama breach adds fuel to a growing narrative among critics and retail participants alike: the persistent sentiment that many cryptocurrency exchanges suffer from inadequate security infrastructure and subpar management systems that fail to protect user digital assets and personal data effectively.
At the same time, industry analysts point out that while such breaches attract intense media scrutiny, many of these cases remain isolated events. The broader market features massive, globally recognized cryptocurrency exchanges—such as Binance, Coinbase, and Gemini—that have implemented rigorous, institutional-grade security standards and compliance frameworks, maintaining unblemished records of operational safety since entering the industry.
 Azzam Bilal Chamdy
 Nila Kartika Wati