
 By Laily UPN
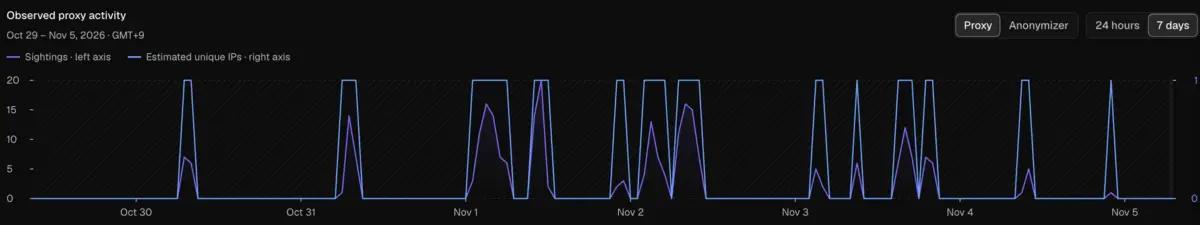
Security experts have revealed a startling operational security lapse within the highest levels of the United States government, discovering that multiple devices connected to the official White House network have been silently functioning as commercial proxy nodes. This configuration potentially allows paying strangers anywhere in the world to route their internet traffic through the Executive Office of the President.
According to findings released by cybersecurity firms Layer3 Intel and Synthient, staff members inside the White House have been using computers or mobile devices equipped with residential proxy applications. These background services monetize a user’s internet connection by rendering their IP address available to third-party renters. Among the services detected beaconing from the dedicated White House network is Infatica, a proxy provider founded by Vladimir Fomenko, a Russian national whose former web hosting firm was famously implicated in cyberattacks targeting state election systems in Arizona and Illinois in 2016.
The discovery underscores a sweeping, systemic threat facing both corporate and government networks: the infiltration of consumer-grade proxy services onto highly sensitive infrastructure via employee devices brought into the workplace.
The security firm Layer3 Intel reported that it first detected multiple residential proxy nodes beaconing outward from the specific internet address block reserved for the Executive Office of the President, designated as AS2650. The firm’s telemetry indicated that the proxy activity was relatively persistent over a one-month observation window, occurring between October 5 and November 3. A rigorous review of the available proxies running on AS2650 showed that traffic successfully exited from the White House network 236 times during that active period.
Simultaneously, proxy tracking company Synthient shared analyses indicating that the mysterious traffic originating from AS2650 was directly tied to multiple Windows 11 installations running Infatica. This proxy program is frequently bundled into seemingly innocuous, free mobile and desktop applications. Software developers often integrate software development kits provided by residential proxy networks into their products to monetize their user bases, granting developers a fraction of a cent or a small financial payout for each installation. Unwitting users rarely realize that installing a free utility or game might turn their device into an active gateway for global internet traffic.
The background of Infatica’s leadership has drawn immediate scrutiny from intelligence and security observers. Fomenko, the founder of Infatica, previously operated King Servers. In 2016, King Servers made international headlines when cybersecurity investigators discovered that six of the eight internet addresses utilized by Russian state security services to breach and compromise databases belonging to election systems in Illinois and Arizona were hosted on Fomenko’s infrastructure.
While dozens of residential proxy providers exist today with varying degrees of legitimacy, many operate out of jurisdictions like Russia and China. Regardless of their origins, they all share a core operational mechanism: they make it simple and inexpensive for external customers to rent another person’s residential or corporate internet address to anonymize web traffic or spoof physical geographic locations. To any destination website or service, web traffic routed through a proxy network appears
to originate directly from the rented IP address rather than from the actual end user of the proxy service.
Layer3 Intel’s analysis revealed that the unauthorized proxy exit nodes operating out of the White House network originated from six distinct internet addresses, appearing across 26 out of 30 surveyed days. Notably, the vast majority of this activity occurred during evening hours, specifically between 5:00 p.m. and midnight, a pattern consistent with employees bringing professional or personal devices home or using corporate hardware for personal tasks outside of core working hours.
Perhaps most alarming to cybersecurity researchers is that Infatica was not an isolated anomaly on the network. Layer3 Intel discovered that a staggering 28 separate residential proxy services were capable of routing traffic and exiting through the high-security government network.
Describing how the network was uncovered, the Layer3 Intel research team noted that the exposure was entirely public and unrestricted. Anyone could theoretically obtain access by signing up for a public residential proxy service, paying a minimal fee, and routing web requests through the network. The researchers emphasized that they did not selectively target the White House network or attempt to force their probes to exit through it; rather, they stumbled upon the vulnerability purely by chance while requesting global rotating access through these commercial services.
The White House did not immediately respond to requests for comment regarding the security findings.
Over the past several years, security researchers have documented how residential proxy services function as a primary engine for unwanted and malicious internet traffic. These networks are frequently weaponized to facilitate account takeover attacks, financial fraud, advertising scams, and mass content scraping operations designed to feed data-hungry artificial intelligence projects.
Beyond fraud, these services introduce severe technical vulnerabilities into the local networks where they reside. In late 2025, security analysts discovered that cybercriminals were heavily exploiting widespread vulnerabilities inherent in many residential proxy platforms. Attackers used these flaws to systematically probe local networks attached to proxy endpoints, searching for vulnerable systems to infect with malware. By January 2026, dozens of proxy providers were forced into emergency patching cycles after Synthient founder Ben Brundage demonstrated how threat actors were actively abusing proxy service vulnerabilities to hijack total control over devices sitting safely behind the firewalls of unsuspecting users.
Brundage noted that the economics of the proxy market exacerbate the danger, explaining that some resellers sell bandwidth for as little as sixty cents per gigabyte. For less than a dollar, malicious actors can essentially purchase a bridge directly into some of the most confidential, trusted networks in the world. Furthermore, the sprawling ecosystem of unregulated resellers often allows criminals to bypass standard Know Your Customer verification processes entirely, purchasing access with minimal friction or oversight.
Despite these catastrophic risks, residential proxies are remarkably commonplace across corporate and government IT environments. Data from a January 2026 webinar hosted by proxy tracking service Spur revealed that residential proxy nodes were detected in nearly 300 government-owned and operated networks, alongside 318 utility companies, 166 healthcare organizations and hospitals, and 141 financial and banking institutions. Additionally, a report published earlier this year by security firm Infoblox indicated that fully 65% of its corporate customer base had endpoints querying one or more residential proxy-related domains, illustrating a pervasive blind spot in modern network perimeter defense.
 Asro
 Ammar Sabilarrohman