
 By Basiran
A teenager from Amman, Jordan, suspected of orchestrating the operations of the prolific data theft and extortion syndicate known as ShinyHunters, has been detained by local authorities and is reportedly cooperating with the Federal Bureau of Investigation (FBI) to identify other members of the hacking collective.
According to reports from KrebsOnSecurity, the suspect—who operates online under the hacker handle "Rey"—was taken into custody just as the ShinyHunters group was actively attempting to extort a business unit recently divested by the global aerospace giant Boeing. In a striking convergence of digital crime and personal proximity, the targeted company manufactures the fleet of aircraft utilized by the employer of Rey’s father, Royal Jordanian Airlines.
The international dragnet tightened on October 3, when Reuters cited three unnamed sources confirming that a suspected ShinyHunters member in Amman named Saif Al-din Khader had been detained by Jordanian authorities and was providing assistance to the FBI. KrebsOnSecurity previously identified Rey as Khader in a November profile published in 2025, during which the young man openly admitted to collaborating with multiple ransomware operations.
Rey’s activities captured headlines once again in a September exclusive detailing the arrest of 24-year-old convicted Dutch cybercriminal Pepijn van der Stap by police in the Netherlands. Van der Stap was apprehended on suspicion of facilitating data thefts and extortion campaigns orchestrated by ShinyHunters.
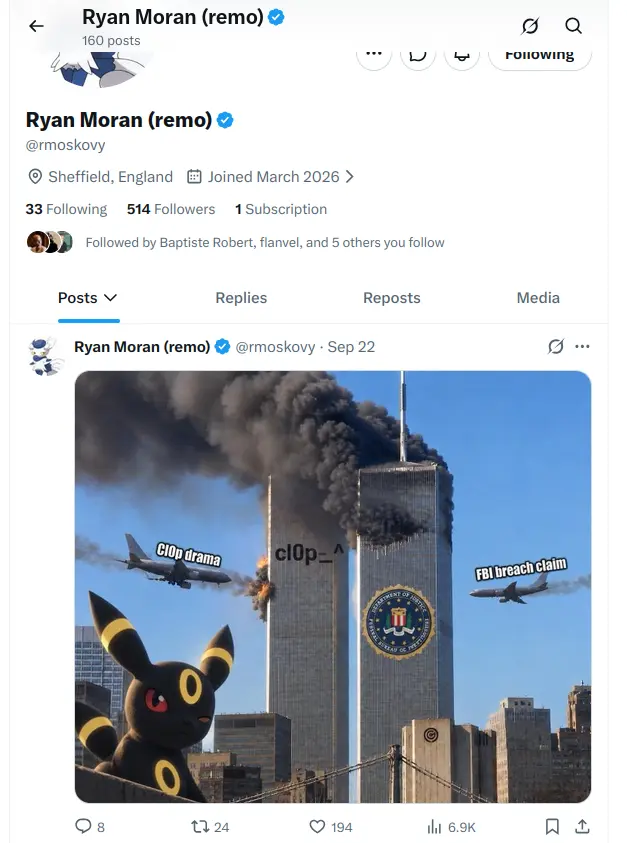
According to investigative findings, immediately following the Dutchman’s arrest on the evening of September 15, Rey stepped forward to assume control of the ShinyHunters brand. In a brazen public display, he began boasting online about stealing highly sensitive data from the FBI and attempting to extort the notorious ransomware group known as Cl0p.
Rey targeted both the FBI and Cl0p with custom memes published via his long-standing Twitter/X account. Simultaneously, he embedded images of the avatar used by Van der Stap’s former hacker alias, "Umbreon," in what investigators believe was a calculated attempt to frame the Dutch national for both high-profile breaches.

The PeopleSoft Vulnerability and Corporate Fallout
The security breaches targeting the FBI and other corporate entities were executed by exploiting a critical zero-day vulnerability, tracked as CVE-2026-35273, residing in PeopleSoft. PeopleSoft is a widely utilized software-as-a-service platform developed by tech giant Oracle, heavily relied upon across global industries for human resources management, payroll administration, hiring pipelines, and employee benefits.
Oracle swiftly issued a software patch after ShinyHunters began mass-exploiting the zero-day flaw in June. Simultaneously, cybersecurity firm Mandiant released specialized web application firewall (WAF) rules designed to protect organizations that were unable to apply the security update immediately.
While ShinyHunters initially told media outlets in June that their primary objective was to breach the FBI’s proprietary PeopleSoft database—an attempt that hackers claimed was ultimately unsuccessful—the group later adapted. In subsequent weeks, ShinyHunters bypassed Mandiant’s defensive measures by deploying a well-known URL-encoding trick to circumvent the recommended WAF rules.
In a joint threat intelligence report released on September 25, security experts at Mandiant and the Google Threat Intelligence Group (GTIG) confirmed that ShinyHunters had mass-exploited the PeopleSoft vulnerability. The campaign successfully compromised data across dozens of systems spanning a diverse range of critical sectors, including higher education, healthcare, technology, agriculture, transportation, and government agencies.
Further compounding the fallout, Reuters reported that the FBI removed an Accenture contractor over failures to patch the agency’s recruitment portal. The compromised portal exposed sensitive records belonging to more than 5,000 FBI personnel, including individual unit assignments, professional specializations, and confidential medical and psychiatric records.
‘Rey’ Means King, as in Royal
Investigators familiar with the ongoing ShinyHunters probe revealed that a navigation and digital aviation unit recently divested by Boeing was among the active targets of the group’s extortion attempts at the time of Rey’s apprehension. The inclusion of a former Boeing subsidiary in the extortion campaign lent renewed urgency to the FBI’s investigation, as the stolen data posed potential operational safety and security risks.

In a statement provided to cybersecurity researchers, Boeing acknowledged the extortion attempts, confirming that the incident involved data stolen from Jeppesen ForeFlight. Boeing had previously sold the subsidiary to private equity firm Thoma Bravo in November 2025 for $10.55 billion.
"We are aware of claims by a threat actor regarding data allegedly associated with Boeing and our former subsidiary Jeppesen ForeFlight," a Boeing spokesperson stated. "Estamos actively reviewing the matter with the Jeppesen ForeFlight team."
Jeppesen ForeFlight maintained that its core systems remained secure. A company spokesperson noted in a written statement that an internal investigation revealed no operational or product impact stemming from the extortion claims.
Rey’s alleged involvement in targeting the former Boeing unit carries personal irony, given substantial evidence indicating his father is employed by Royal Jordanian Airlines. The airline is majority-controlled by the Jordanian government and operates its long-haul passenger fleet using aircraft built by Boeing. Although unconfirmed independently, Rey claimed on Telegram in early 2025 that his father worked as an airline pilot.
Furthermore, forensic analysis of a shared family computer—compromised previously by password-stealing malware—revealed that Rey’s father utilized identical credentials across multiple online portals for Royal Jordanian Airlines employees.
Following inquiries from investigative journalists, Rey began rapidly purging his digital footprint, deleting numerous social media profiles, including the Twitter/X account used to mock law enforcement and rival cybercriminal syndicates. Despite scrubbing his social channels, Rey’s cybersecurity blog hosted on GitHub remained active, featuring technical investigations, including a March post that attempted to dox two Russian men alleged to be the core operators behind the Cl0p ransomware platform.

Murder-for-Hire Allegations in the Netherlands
Meanwhile, legal proceedings in the Netherlands introduced explosive new allegations against Pepijn van der Stap, whose narrative of personal rehabilitation following a prior conviction had previously gained traction in technology media circles. Dutch daily newspaper RTL reported that investigators suspect Van der Stap attempted to orchestrate at least two murders. According to the reports, the planned attacks were directed to take place abroad, and authorities uncovered indications that Van der Stap issued the orders.
Van der Stap had recently completed the majority of a four-year prison sentence stemming from historical data theft and extortion activities that prosecutors estimated yielded between 1.5 million and 2.7 million euros. Prior to his September arrest, Van der Stap participated in interviews claiming he had transitioned into a legitimate cybersecurity career, working as an "offensive security lead" at Neo Security to test client networks for vulnerabilities.
Benjamin Korper, the owner of Neo Security, stated that he retained an external firm to audit his company’s infrastructure for signs of unauthorized access by Van der Stap. Thus far, independent investigators have uncovered no evidence indicating the former convict compromised his employer or clients. Korper confirmed that Dutch forensic officers raided his corporate offices on the night of September 15, an operation local media reported involved the deployment of flash-bang grenades.
Before his initial arrest in 2023, Van der Stap worked as a software engineer for Amsterdam-based cybersecurity startup Hadrian and volunteered with the Dutch Institute for Vulnerability Disclosure (DIVD), even while quietly orchestrating cyberattacks against major international organizations.
When questioned about how the public could trust a self-described reformed cybercriminal, Van der Stap maintained that his technical output must stand on its own merit. "You can throw a bunch of nice words at someone, but you can’t convince them if they don’t want to be convinced," Van der Stap stated prior to his arrest. "I’m doing what I can to repay victims, and that’s all I can do."
Franchising and Burning a Brand
Cybercriminals operating under the ShinyHunters banner have been linked to dozens of major data breaches stretching back to 2019, compromising billions of individual records. However, security researchers emphasize that the individuals currently wielding the ShinyHunters moniker bear little relation to the group’s original core members, most of whom are French nationals who have faced arrest and prosecution.

Experts note that ShinyHunters has evolved into an ideological and operational franchise. Much like the literary concept of the Dread Pirate Roberts, succession within the cybercrime syndicate occurs not through voluntary retirement, but through law enforcement intervention, often leaving multiple individuals claiming the mantle simultaneously. Investigators indicate that the FBI’s primary focus centers on a network of freelance affiliates who feed stolen SaaS platform credentials to the group in exchange for a percentage of subsequent extortion payouts.
In the wake of Van der Stap’s arrest, underground Telegram channels operated by Rey became arenas of internal friction. Participants mocked the teenage hacker after he retreated from public threats directed at the FBI and Cl0p, and as the group’s darknet portal abruptly went offline. Critics within the cybercrime ecosystem accused Rey of usurping the defunct ShinyHunters brand for personal financial gain.
"He bought the old forum PGP key and used it to make new Breachforum websites and Telegram channels larping as ShinyHunters to ransom companies and then sell the used data or resell his forum when he goes broke," one community member alleged.
A dedicated tracking channel on Telegram known as "The Battle" has spent weeks doxing and ridiculing Rey and other alleged affiliates. Administrators of the channel criticized Rey for attempting to leverage a dismantled syndicate’s reputation to inflate his standing.
"Rey made a serious mistake when he started pretending to be a member of ShinyHunters," write the administrators of The Battle. "That group had already been dismantled, with many of its members either arrested or imprisoned, yet Rey still chose to use its name while carrying out his crimes."
In interviews with technology publications, representatives for ShinyHunters asserted that their decision to target high-profile entities like the FBI was driven by a desire to counter law enforcement advisories discouraging ransom payments. Despite their public bravado, security analysts and industry researchers maintain that coordinated international law enforcement pressure, combined with structural fractures within underground affiliate networks, has severely degraded the operational viability of the ShinyHunters brand.
 Asro
 Ammar Sabilarrohman
 Laily UPN