
 By Jia Lissa
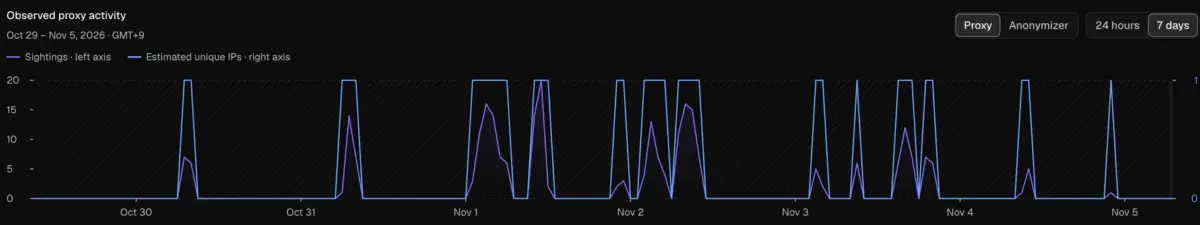
Security researchers have issued a startling warning after discovering that several staff members at the White House are using computers or mobile devices equipped with residential proxy services. These commercial programs effectively render their official internet addresses available for rent to outside parties, creating an unprecedented cybersecurity vulnerability within the highest levels of the United States government.
According to threat intelligence findings released today, one of the primary residential proxy services detected on the Executive Office of the President’s network is operated by a Russian company. Most concerningly, the founder of this proxy firm previously ran a web hosting business that served as ground zero for infamous cyberattacks targeting state election systems in Arizona and Illinois back in 2016.
The security firm Layer3 Intel announced that it detected multiple residential proxy nodes beaconing out directly from the specific internet address block reserved for the Executive Office of the President, designated formally as AS2650. In its technical analysis, Layer3 reported that the proxy activity was relatively persistent over a month-long observation window, occurring between October 5 and November 3. During this period, a comprehensive review of the active proxies available through AS2650 revealed that they successfully exited from the heavily guarded White House network no fewer than 236 times.
Simultaneously, the proxy tracking and threat intelligence company Synthient published data on social media indicating that the suspicious activity originating from AS2650 was directly tied to multiple Windows 11 installations of a service known as Infatica. Infatica is a commercial proxy program that is frequently bundled or integrated into seemingly harmless "free" mobile applications and desktop software.
The background of Infatica’s leadership adds a severe geopolitical and counterintelligence dimension to the discovery. The firm was founded by Vladimir Fomenko, a Russian national whose previous web hosting company, King Servers, was identified by investigators as the infrastructure provider for six out of the eight specific internet addresses utilized by Russian state security services. Those addresses were deployed during the 2016 operation to compromise sensitive databases belonging to election systems in Arizona and Illinois.
Residential proxy providers operate in a complex ecosystem characterized by varying degrees of legitimacy, with a significant concentration of operators based in foreign jurisdictions such as China and Russia. However, regardless of their stated intent, all of these services share a core functionality: they make it remarkably simple for paying customers to rent another user’s genuine residential or corporate internet address. This setup allows individuals to anonymize their web traffic or thoroughly spoof their true geographic location. From the perspective of any website or external server receiving the traffic, the connection appears to originate from the rented IP address—such as one belonging to the White House—rather than from the actual proxy service customer or malicious actor sitting behind it.
Layer3 Intel’s telemetry revealed that the unauthorized proxy exit nodes operating out of the White House network utilized six distinct internet addresses across 26 of the 30 days monitored by the firm. Furthermore, the researchers noted a distinct temporal pattern to the activity, observing that the vast majority of the proxy connections occurred during evening hours, specifically between 5 p.m. and midnight local time.
Incredibly, Infatica was far from the only commercial proxy service found to be reselling access to White House internet addresses. Layer3 Intel stated that its investigative probes uncovered a staggering 28 separate residential proxy services that were capable of routing traffic and exiting through this dedicated government network.
Describing the ease with which outside entities could leverage this infrastructure, the Layer3 Intel research team wrote that the situation amounted to public access. They noted that anyone could obtain access simply by signing up for a public residential proxy service, paying a nominal fee of a few dollars, and routing web requests through the network. The researchers emphasized that they did not selectively target the White House network or attempt to force their monitoring probes to exit from it; rather, they stumbled upon the vulnerability by chance while requesting global rotating access through these commercial services as part of routine tracking.
When contacted for comment regarding the security findings, the White House did not immediately respond.
The discovery highlights a pervasive and growing threat that has been tracked closely over the past year. Residential proxy services have increasingly become a major source of unwanted, disruptive, and outright malicious traffic across the global internet. This includes cybercrime activities such as account takeovers, sophisticated advertising fraud, and mass content scraping operations designed to feed data to artificial intelligence projects.
Beyond the baseline risks of traffic spoofing, these services can introduce severe vulnerabilities to local networks. In late 2025, security researchers discovered that cybercriminals were heavily exploiting widespread architectural flaws in residential proxy networks. These vulnerabilities allowed bad actors to systematically probe each proxy endpoint’s local network for unpatched or vulnerable systems to infect with malware.
The danger was further underscored in January 2026, when dozens of proxy services were forced to implement emergency patches after Synthient Founder Ben Brundage demonstrated how cybercriminals were weaponizing these weaknesses. Attackers were abusing residential proxy infrastructure to achieve remote control over devices located securely inside the local networks of unsuspecting users, bypassing traditional perimeter defenses entirely.
Brundage emphasized the extreme affordability and accessibility of these attack vectors to KrebsOnSecurity, pointing out that some proxy resellers sell bandwidth for as little as sixty cents per gigabyte. This economic model means that for less than a dollar, an adversary can gain direct access into some of the most confidential and trusted networks in the world. He added that the broader reseller ecosystem actively facilitates this risk by allowing anonymous cybercriminals to purchase high-value access while completely bypassing Know Your Customer and identity verification protocols.
The root cause of these network exposures frequently traces back to employee behavior in the workplace. All too often, these proxy capabilities are introduced onto corporate or government networks via employee devices brought from home. Software and app developers routinely embed software development kits supplied by residential proxy networks into consumer applications as a monetization strategy, enabling the developers to receive a small financial payout for every successful installation, often without the user fully understanding the network implications.
While the presence of residential proxies inside the White House represents an extreme national security concern, the phenomenon is surprisingly widespread across critical sectors of the economy and government. Data shared by proxy tracking service Spur during a webinar earlier this year revealed that residential proxy nodes were detected operating inside nearly 300 government-owned and operated networks. Additionally, the tracking revealed active proxies within 318 utility companies, 166 healthcare organizations and hospitals, and 141 firms operating within the sensitive banking and finance sectors. Complementing these findings, a security report published by Infoblox earlier this year indicated that fully 65 percent of its enterprise customer base had corporate networks querying one or more residential proxy-related domains.
 Asro
 Ammar Sabilarrohman
 Laily UPN